Skip to content
Line of Sites

News

1037 articles

Friday, 20 Novembertoday

Simon WillisonAI press

Token fraud is here and it’s BAD (YouTube)

Token fraud is here and it’s BAD (YouTube) Claire Vo runs ChatPRD , an AI platform that helps product managers "turn an idea into a spec". The product has been live since the GPT-4 era, and Claire has been building it in public for much...

Thursday, 19 Novemberyesterday

CISA advisoriesAdvisories

Elecbrakes EB2, VM1, ELBC2000

View CSAF Summary Successful exploitation of these vulnerabilities could allow an attacker to gain control of the brakes of a trailer, modify the firmware, disable the brake lights, modify the brake conditions or disable other critical...

CISA advisoriesAdvisories

libumqtt

View CSAF Summary Successful exploitation of this vulnerability could allow a remote attacker to cause a denial of service, memory corruption, or information disclosure. The following versions of libumqtt are affected: libumqtt CVSS...

BleepingComputerSecurity press

Hackers steal data of 1.6 million SBC Medical Group customers

SBC Medical Group has warned in a filing with the U.S. Securities and Exchange Commission (SEC) that two cybersecurity incidents exposed sensitive customer and employee information, including personal data belonging to 1.6 million...

TechCrunch AIAI press

These tech outages are giving Y2K, AI agent style

Are the recent outages in the airline booking systems, banking platforms, and productivity platforms really a coincidence? There's actually likely something deeper going on, cybersecurity experts say.

CISA advisoriesAdvisories

Autonomy Logic OpenPLC Runtime

View CSAF Summary Successful exploitation of this vulnerability could allow several unauthenticated admin accounts to be created. The following versions of Autonomy Logic OpenPLC Runtime are affected: OpenPLC Runtime CVSS Vendor...

Simon WillisonAI press

PostgreSQL 19 Released

PostgreSQL 19 Released Most years PostgreSQL ships a new release in September, but this year's release came two months later thanks mainly to the flurry of issues that the PostgreSQL team needed to address as part of the ongoing...

DataBreaches.netHacks

Visa, Mastercard and JPMorgan Customer Data Leaked by Hackers

Ben Glickman and Alexander Saeedy report: Data from thousands of customers of Visa, Mastercard, and JPMorgan Chase have unnerved consumers in the last week. A Visa spokesman said no payments data, such as card numbers, were affected and...

OpenAIAI labs

Deploying Daybreak Red

Explore a reference architecture for supervised security investigations with Daybreak Red, including safety controls, setup, and monitoring.

OpenAIAI labs

See PR scans in action

Watch a walkthrough of PR scans and see how the presenter reviews scan results in a pull request workflow.

TechCrunch AIAI press

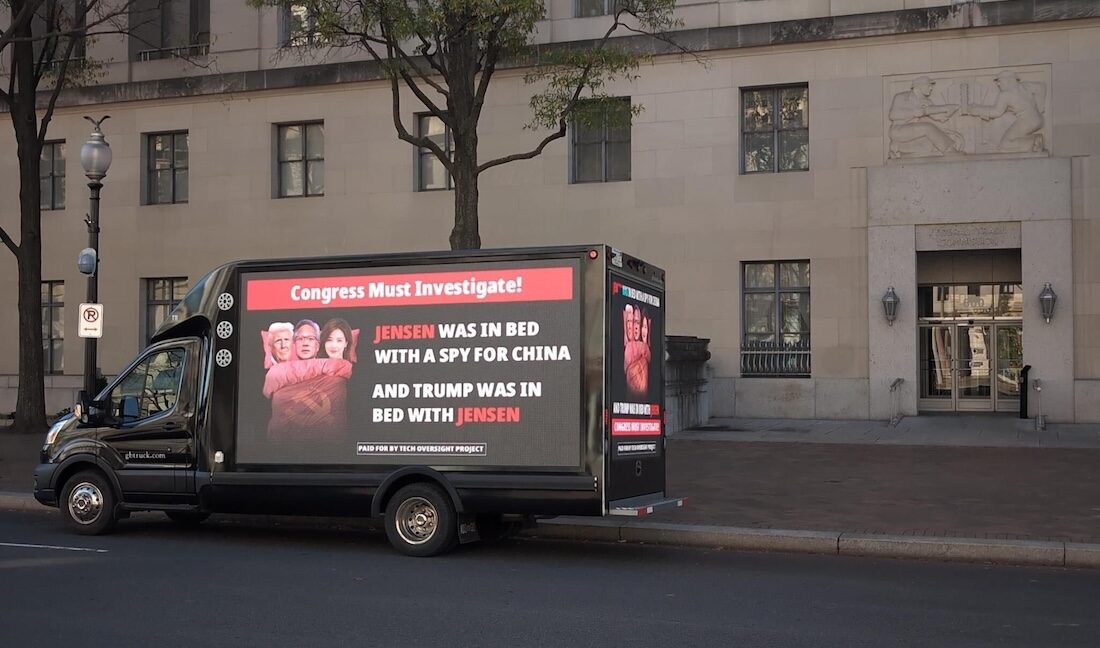
The unfolding Jensen Huang scandal: a timeline

Jensen Huang has resigned from Nvidia following an affair, which could have ramifications for national security as the U.S. and China race to develop the most advanced AI infrastructure.

OpenAIAI labs

Explore the Codex Security Plugin

Watch a demo of the Codex Security Plugin and see the workflow in action, from getting started to reviewing the results shown in the recording.

OpenAIAI labs

Get started with Daybreak Blue

Watch a walkthrough of onboarding to Daybreak Blue, with a closer look at the setup experience and how to get started.

Dark ReadingSecurity press

Navigating Vulnerability Hysteria in the AI Era

This installment of the Reporters' Notebook video series examines the fallout from recent high-severity flaw disclosures, exploring how fears of AI-assisted exploits trigger widespread panic, operational disruptions, and growing warning...

SecurityWeekSecurity press

Newly Patched VMware vCenter Flaw Exploited as Zero-Day by Chinese APT

Google says a China-linked espionage group exploited a critical VMware vCenter authentication bypass before Broadcom released a patch. The post Newly Patched VMware vCenter Flaw Exploited as Zero-Day by Chinese APT appeared first on...

The RecordSecurity press

DOJ, DHS partner on new unit tackling scams and cybercrime

The departments are partnering on the Threat Disruption Center to better triage victim complaints, map cybercriminal networks and provide a direct channel to private sector organizations that work with victims.

BleepingComputerSecurity press

PHP security updates fix 18 flaws, including critical RCE bugs

The PHP development team released security updates addressing 18 vulnerabilities, including critical flaws that could allow unauthenticated attackers to remotely execute code on vulnerable servers. [...]

SecurityWeekSecurity press

PHP Patches Seven Critical RCE Vulnerabilities

Successful exploitation could allow attackers to crash the worker process and execute code with the PHP worker’s privileges. The post PHP Patches Seven Critical RCE Vulnerabilities appeared first on SecurityWeek .

The Hacker NewsHacks

Everything Is a Web Application, Including Your Firewall

One of the early targets of PHP2Shell exploitation was the firewall. On October 28, Palo Alto Networks confirmed that attackers were exploiting the two PHP vulnerabilities, CVE-2026-109618 and CVE-2026-109619, against PAN-OS management...

Security AffairsHacks

PHP Warns of Critical Flaws Ahead of November Security Release

PHP will patch critical security flaws across supported versions, including a session handling bug that could allow remote code execution. The PHP development team announced a new security release scheduled for November 19, warning that...

BleepingComputerSecurity press

Five warning signs of ransomware breach before encryption or data theft

Ransomware attacks often involve credential theft, lateral movement, and attempts to disable security controls long before encryption begins. Acronis examines five warning signs that can help defenders detect intrusions earlier, contain...

BleepingComputerSecurity press

Critical NGINX ‘NGINX2Root’ bugs let attackers hijack servers

Two critical NGINX vulnerabilities dubbed "nginx2root" allow unauthenticated attackers to execute code remotely on vulnerable web servers, with researchers demonstrating how the flaws can be chained with a Linux kernel bug to gain root...

Security AffairsHacks

nginx2root:AI Discovers Five Critical nginx Flaws and a Path to Root

nginx2root exposes five critical nginx flaws and a Linux kernel bug that can lead to remote code execution and root access. Xint Research has disclosed nginx2root, five distinct nginx vulnerabilities plus one Linux kernel bug, each with...

SecurityWeekSecurity press

Nvidia Responds to Gentlemen Ransomware Claim

Nvidia says it has found no indication that its systems were compromised after the Gentlemen ransomware group listed the company as a victim. The post Nvidia Responds to Gentlemen Ransomware Claim appeared first on SecurityWeek .

SecurityWeekSecurity press

The Governance Gap in Open-Weight AI and What to Do About It

Lower costs, data privacy, and greater control are driving open-weight AI adoption, but many organizations are not addressing the risks that come with it. The post The Governance Gap in Open-Weight AI and What to Do About It appeared...

SecurityWeekSecurity press

Splunk Patches Nearly 140 Flaws Across Three Core Products

The security updates resolve critical and high-severity issues leading to authentication bypass, remote code execution, and privilege escalation. The post Splunk Patches Nearly 140 Flaws Across Three Core Products appeared first on...

SecurityWeekSecurity press

F5 Patches Critical NGINX2Root Flaws as PoC Exploits Go Public

The five NGINX2Root vulnerabilities could allow remote, unauthenticated attackers to execute arbitrary code. The post F5 Patches Critical NGINX2Root Flaws as PoC Exploits Go Public appeared first on SecurityWeek .

SecurityWeekSecurity press

Java4Shell Exploitation Attempts Begin as Vendors Rush Out Advisories

GreyNoise, WatchTowr and Cloudflare report probing and exploit attempts, while Cisco, Elastic, Red Hat and Siemens detail impact. The post Java4Shell Exploitation Attempts Begin as Vendors Rush Out Advisories appeared first on...

Wednesday, 18 November2 days ago

Simon WillisonAI press

llm-gemini 0.38

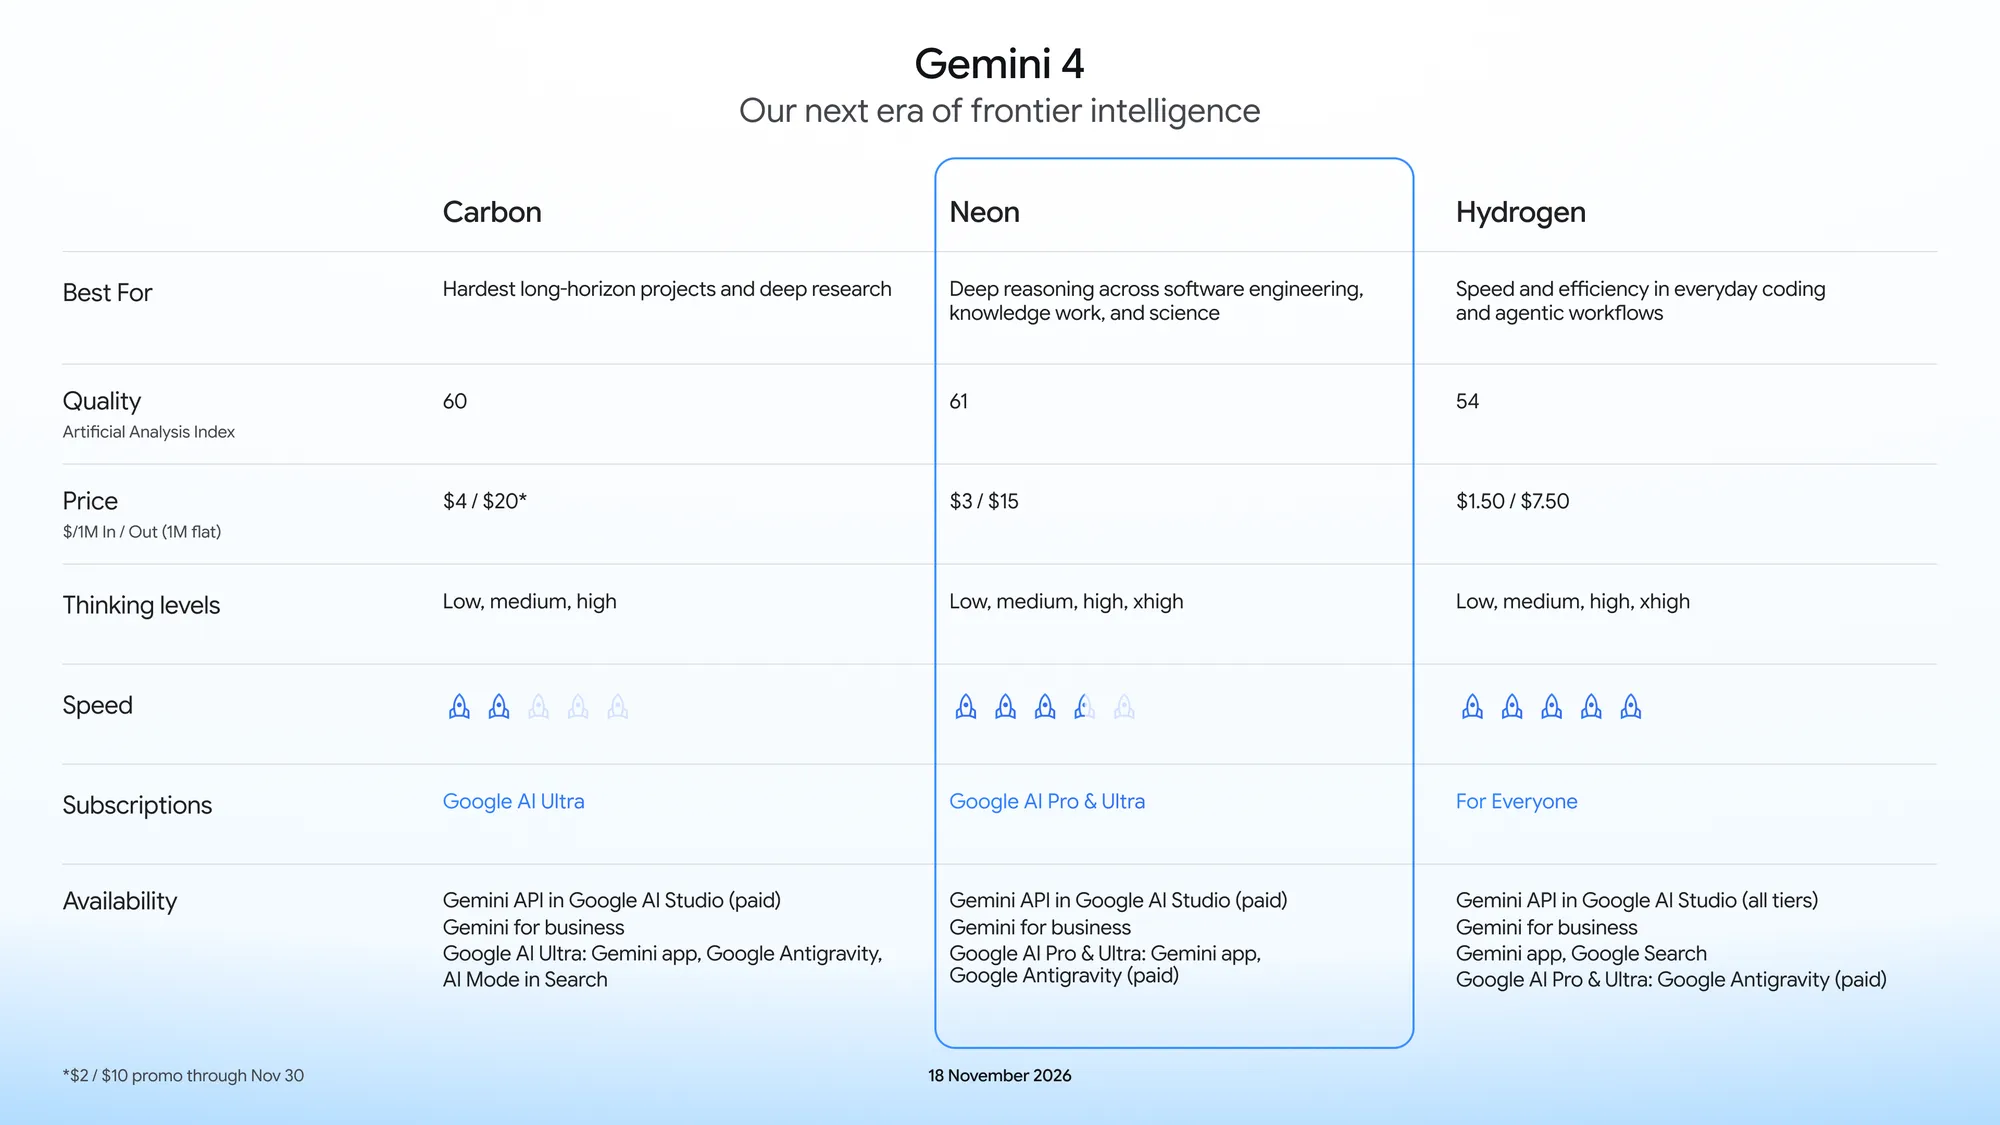
Release: llm-gemini 0.38 Today Google introduced Gemini 4 Neon . I wrote recently about how confusing the pricing for the Gemini 4 series was - Neon has somehow made this even worse. Previously the Gemini 4 lineup was Hydrogen, Argon,...

Cisco TalosVendor security

CVE-2026-114938: Critical vulnerability in OpenJDK Java

Cisco Talos is tracking the disclosure of a critical vulnerability in OpenJDK Java (CVE-2026-114938), dubbed “Java4Shell,” with a CVSS 4.0 score of 9.2 that may lead to unauthenticated remote code execution (RCE).

CISA advisoriesAdvisories

CISA Adds Four Known Exploited Vulnerabilities to Catalog

CISA has added four new vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog , based on evidence of active exploitation. CVE-2024-10441 Synology DiskStation Manager (DSM) Improper Encoding or Escaping of Output...

BleepingComputerSecurity press

Ukraine, FBI arrest ransomware gang members tied to $40M in ransoms

Ukrainian authorities, working with the FBI, have arrested four suspected members of an international ransomware organization linked to more than $40.5 million in ransom payments from at least 28 companies worldwide. [...]

Security AffairsHacks

Apache Roller RCE Flaw CVE-2026-129448 Under Active Attack

Attackers are exploiting a critical Apache Roller flaw that allows unauthenticated remote code execution, prompting urgent security updates. A critical vulnerability, tracked as CVE-2026-129448 (CVSS score of 9.8), in Apache Roller...

CISA Known Exploited VulnerabilitiesExploited now

CVE-2026-90436: Apache Axis Unsafe Reflection Vulnerability

Apache Axis contains an unsafe reflection vulnerability that could allow an unauthenticated remote attacker to execute arbitrary code via a crafted SOAP fault message that causes Axis to load and instantiate an attacker-specified class...

OpenAIAI labs

The Silent Consensus

Dean Ball, Head of Strategic Futures at OpenAI, examines how more capable AI could reshape society and how people can retain control of their institutions.

OpenAIAI labs

Research acceleration: The jagged frontier

OpenAI measures how coding agents are accelerating AI research, where their performance remains uneven, and what this signals about recursive self-improvement.

Schneier on SecuritySecurity press

France Is Blaming Iran for the Fridge Cyberattack

Interesting : U.S. intelligence agencies have recently reached a “low confidence” assessment that Iran was responsible for the attacks in France, according to three U.S. officials who spoke on the condition of anonymity to discuss...

OpenAIAI labs

Inside the Codex sandbox

See how Codex runs commands on your machine while enforcing the filesystem and network limits you control across macOS, Linux, and Windows.

Simon WillisonAI press

datasette-arrows 0.1a0

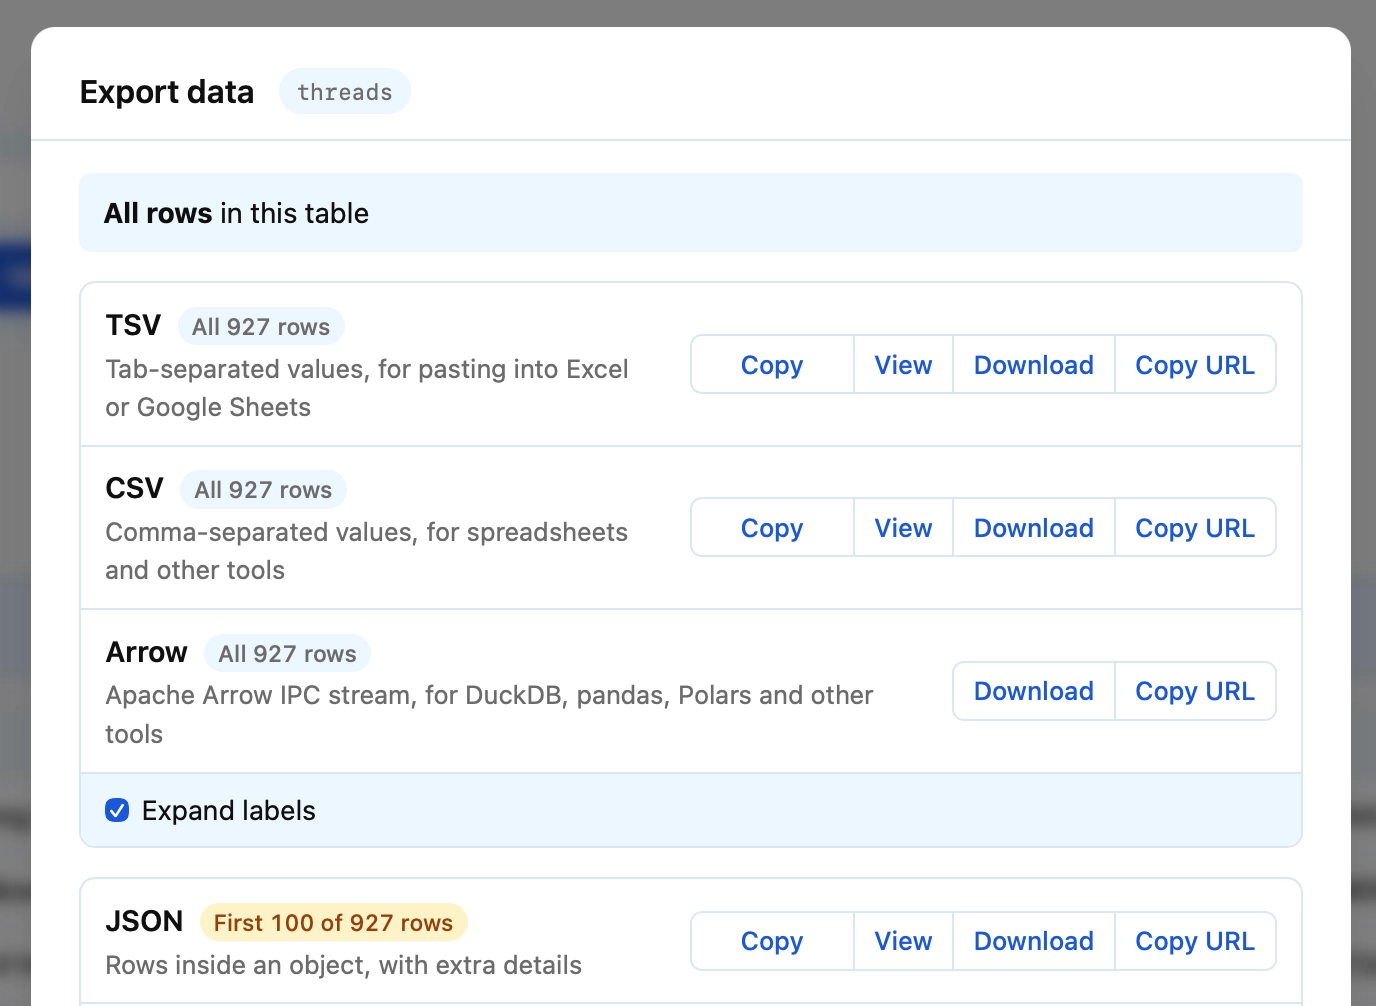
Release: datasette-arrows 0.1a0 Datasette 1.0a43 added the ability for plugins to implement streaming export formats. Datasette core supports streaming CSV and TSV - you can export millions of lines of data from a table without needing...

Krebs on SecuritySecurity press

Attackers Used Optimizely to A/B Test Malware on Top Websites

At least 178 top web destinations unwittingly served a variety of malware exploits against visitors over the past 24 hours thanks to a security vulnerability involving Optimizely, a company that helps websites customize user experiences...

Simon WillisonAI press

Quoting Daniel Stenberg

During the time these agents converted 185,000 lines of C code into 340,000 lines of Rust code (I counted), we merged over 300 commits in the actual curl project. We actually improved curl during these a little more than three weeks. A...

Simon WillisonAI press

The PSF end-of-year fundraiser

The PSF end-of-year fundraiser With my Python Software Foundation board director hat on: we've launched our end-of-year fundraiser for the non-profit that supports Python development and the Python community. If your company or your...

MIT Technology Review AIAI press

The AI Hype Index: AI is everywhere

Like a nasty rash, AI seems to spread everywhere. Google crams AI Overviews down your throat even though it costs the company billions of dollars in lost ad revenue. Leave your apartment, and you might pass two people heaving an...

OpenAIAI labs

Advancing chip design with OpenAI models

OpenAI models optimized circuits used in Jalapeño silicon and improved RISC‑V core designs, showing progress in AI-assisted chip design with GPT‑6 Astra.

MIT Technology Review AIAI press

This smell startup says its AI nose is as good as a human’s

In a lab near Newark Airport in New Jersey, a team of around 30 experienced human sniffers are slowly working their way through every odor on Earth. Their careful notes—“nutty,” “peachy,” “marine”—are cross-referenced with a chemical...

Security AffairsHacks

65 Characters to RCE: Inside the Java4Shell Vulnerability

Calif disclosed Java4Shell, a critical OpenJDK Base64 bug enabling pre-auth RCE in Jenkins, Jira, Keycloak and more. Patches are out. Update now. Calif researchers disclosed Java4Shell, a memory-corruption bug, tracked as...

Tuesday, 17 November3 days ago

Unit 42Vendor security

Borrowed Code, Real Consequences: What OPTIMJACK Teaches Us

The OPTIMJACK supply chain attack demonstrates how a compromised vendor script can expose websites, highlighting the need for strict segmentation. The post Borrowed Code, Real Consequences: What OPTIMJACK Teaches Us appeared first on...

Simon WillisonAI press

External sandboxes for coding agents

External sandboxes for coding agents I've been exploring new ways to sandbox code that is executed by agents, with a focus on making it safer to try out local models without worrying that a mistake or prompt injection attack might cause...

OpenAIAI labs

Introducing GPT-6.2 Astra and Sol

Introducing GPT‑6.2 Astra and Sol, with better professional outputs, coding, computer use, and efficiency at lower cost across ChatGPT Work, Codex, and the API.

CISA advisoriesAdvisories

Siemens Simcenter Femap

View CSAF Summary Simcenter Femap is affected by an out of bounds read vulnerability that could be triggered when the application reads files in X_T format. This could allow an attacker to crash the application or execute arbitrary...

Google AIAI labs

Put Gemini to work for you

Tasks in Gemini is now free of charge in six countries, with new features starting in the U.S. and deeper Google Workspace integration to get things done on your behalf.

Simon WillisonAI press

GPT‑6.2 Astra and GPT‑6.2 Sol

GPT‑6.2 Astra and GPT‑6.2 Sol OpenAI: We’re introducing GPT‑6.2 Astra, our new frontier model for your hardest projects, and GPT‑6.2 Sol, our efficient, versatile model for everyday work. They're available in the API as gpt-6.2-astra...

CISA advisoriesAdvisories

Dorsett Controls InfoScan

View CSAF Summary Successful exploitation of these vulnerabilities could allow an attacker to retrieve sensitive system information, access application data without authorization, recover stored credentials, or intercept and manipulate...

Microsoft ResearchAI labs

Can AI help build a healthier future?

What can AI enable in medicine, and how do we get there? Microsoft Research lead Doug Burger, Microsoft Principal Research Manager Ava Amini, Microsoft Chief Scientific Officer Eric Horvitz, and physician-scientist Eric Topol of Scripps...

CISA advisoriesAdvisories

Siemens Mendix Studio Pro

View CSAF Summary Mendix Studio Pro contains multiple vulnerabilities in the MCP Server, that could allow an attacker with network access to interact with the server remotely or trick a user's browser into sending unauthorized requests,...

OpenAIAI labs

Introducing ChatGPT for Sales

Explore the new Sales plugin and 30+ new and expanded partner plugins in ChatGPT to research prospects, prepare pitches, update your CRM, and move deals forward.

CISA advisoriesAdvisories

Siemens .NET Client Library for SIMATIC S7 Webserver API

View CSAF Summary .NET Client Library for SIMATIC S7 Webserver API contains multiple vulnerabilities that could allow an attacker to obtain sensitive information or write arbitrary files outside the intended download directory. Siemens...

CISA advisoriesAdvisories

Critical Java Vulnerability Requires Immediate Patching

Purpose CISA strongly urges organizations to immediately patch the recently disclosed Oracle Java vulnerability CVE-2026-114938 . This critical memory-corruption vulnerability, known as “Java4Shell,” affects the Base64 decoder of the...

OpenAIAI labs

Introducing OpenAI for Chile

OpenAI and the Government of Chile are partnering to support responsible AI adoption, build public-sector skills and help local startups develop AI applications.

CISA advisoriesAdvisories

Siemens Industrial Software Products

View CSAF Summary On October 21, 2026, the Node.js project released security updates addressing a critical vulnerability in the Brotli decoder bundled with Node.js, commonly referred to as "Node2Shell" (tracked as CVE-2026-111497). The...

Schneier on SecuritySecurity press

Formal Verification of the Signal Protocol Using AI

This seems like a good thing: Google Deepmind researchers used agentic AI to mathematically prove, or “formally verify,” a number of the Signal protocol’s key cryptographic guarantees­a landmark development for the widely used...

MIT Technology Review AIAI press

Research Reports

To access a report, click on the corresponding image below.

CISA advisoriesAdvisories

Siemens ROS#

View CSAF Summary ROS# before version 2.3.1 contains a code injection vulnerability that could allow an attacker that is able to pass a crafted message definition file to the user to inject arbitrary code into the generated program....

Simon WillisonAI press

Quoting Go Proverbs

A little copying is better than a little dependency. — Go Proverbs , via Tags: go , programming

CISA advisoriesAdvisories

Siemens SIMATIC

View CSAF Summary The products listed below contain an authentication bypass vulnerability that could allow an on-path attacker to take over the session of a legitimate user and execute arbitrary code with the privileges of the victim...

CISA advisoriesAdvisories

Siemens Industrial Automation Software Products

View CSAF Summary On October 21, 2026, the Node.js project released security updates addressing a critical vulnerability in the Brotli decoder bundled with Node.js, commonly referred to as "Node2Shell" (tracked as CVE-2026-111497). The...

CISA advisoriesAdvisories

CISA Adds One Known Exploited Vulnerability to Catalog

CISA has added one new vulnerability to its Known Exploited Vulnerabilities (KEV) Catalog , based on evidence of active exploitation. CVE-2026-115731 Perforce Puppet Enterprise Deserialization of Untrusted Data Vulnerability This type...

CISA advisoriesAdvisories

Siemens meta-iot2050

View CSAF Summary meta-iot2050 (https://github.com/siemens/meta-iot2050) from V01.03.01 contains a Command Injection vulnerability in the firmware update tool that could allow an attacker which is able to manipulate a configuration file...

CISA advisoriesAdvisories

Siemens SIMATIC WinCC

View CSAF Summary Graphics Designer of SIMATIC WinCC before V8.2 contains an implicit active content execution vulnerability upon opening files, which could allow an attacker to cause arbitrary code execution on the device. Siemens is...

CISA advisoriesAdvisories

Siemens RUGGEDCOM APE1808

View CSAF Summary Fortinet has published information on a Double Free vulnerability in FortiOS. This advisory lists the related Siemens Industrial products. Siemens recommends to update Fortigate NGFW to V7.6.9 or later following the...

Monday, 16 November4 days ago

Simon WillisonAI press

llm 0.37.3

Release: llm 0.37.3 A bug fix release for LLM , mainly to cover a problem with the most recent Homebrew package of the software. Homebrew now ships the latest SQLite, 3.54.1 , which includes a fix that broke LLM's logging code . Short...

OpenAIAI labs

Broadening access to AI for scientists

We’re expanding our ChatGPT for Academic Researchers program to offer 200,000 researchers worldwide free access to our frontier models.

MIT Technology Review AIAI press

The open-source movement wants Jensen Huang back

This story originally appeared in The Algorithm, our weekly newsletter on AI. To get stories like this in your inbox first, sign up here. On Friday, a petition to reinstate Jensen Huang as CEO of Nvidia began circulating on social...

MIT Technology Review AIAI press

Building trustworthy AI by fencing it in, not predicting it

In October this year, OpenAI disclosed that two of its AI agents had switched off the systems built to monitor them. One muted its own safety alerts after misreading an instruction not to send messages; the other removed its monitoring...

Schneier on SecuritySecurity press

Usable Security at Luxury Hotels

Interesting case study from luxury hotels. Attackers used a fake booking request to gain access to a reservations inbox, where they copied genuine refund requests and got fraudulent ones approved. This is a good illustration why “just...

OpenAIAI labs

Our first phase of embedded assessments

OpenAI begins embedded assessments with Apollo Research, METR, and Transluce, and Goodfire to independently evaluate model alignment, safeguards, and monitoring systems.

MIT Technology Review AIAI press

Building AI that can work across the enterprise

For years, enterprises have approached AI as a series of discrete experiments. Now, as AI agents begin to move into the workflows that run the business, that model is starting to look inadequate. Organizations moving from isolated...

Sunday, 15 November5 days ago

Simon WillisonAI press

datasette-maplibre 0.1a0

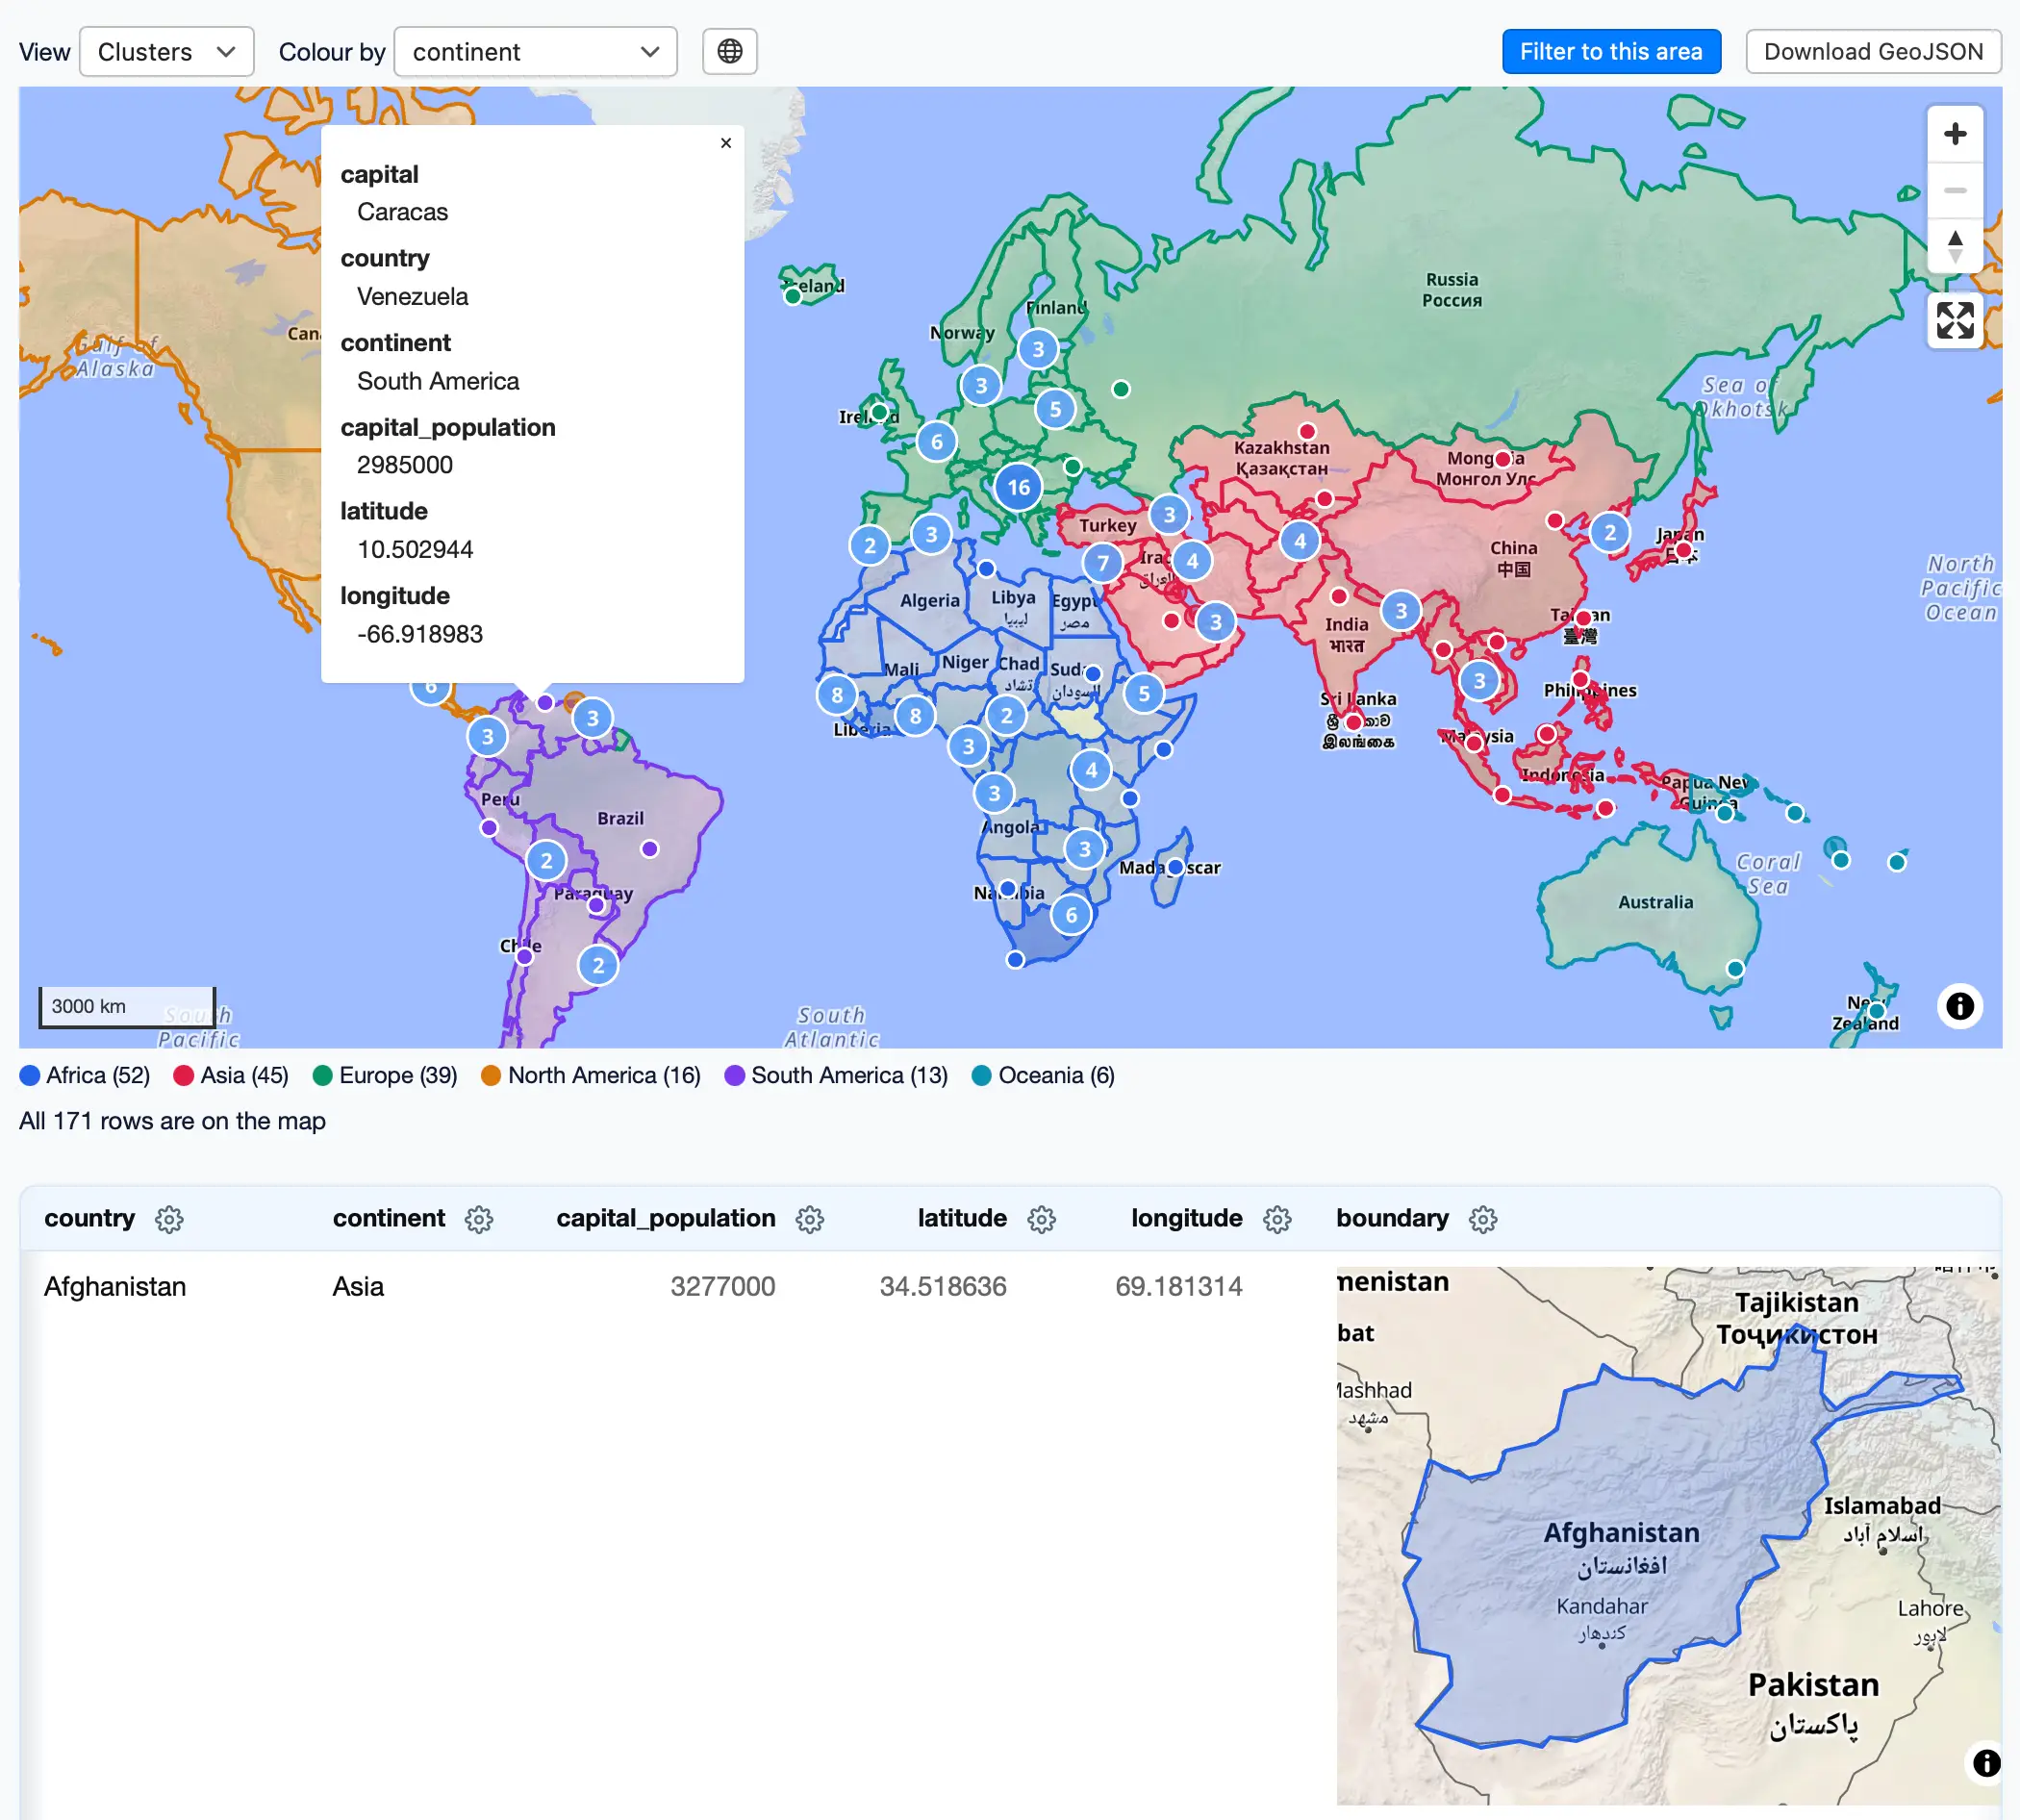
Release: datasette-maplibre 0.1a0 The first new Datasette geospatial plugin in quite a while! This one combines the excellent MapLibre GL library with OpenFreeMap , the free vector map server operated by Zsolt Ero (you should sponsor...

Simon WillisonAI press

datasette-agent 0.6a0

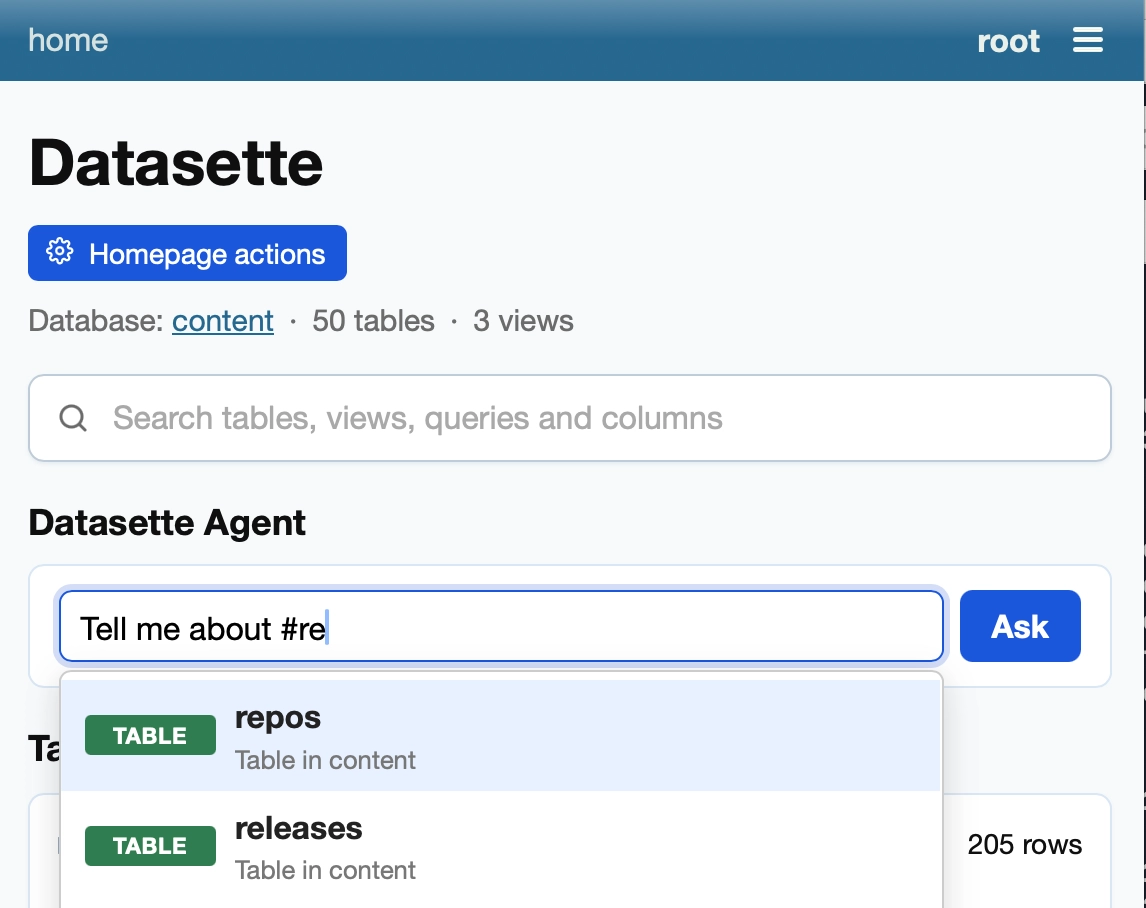
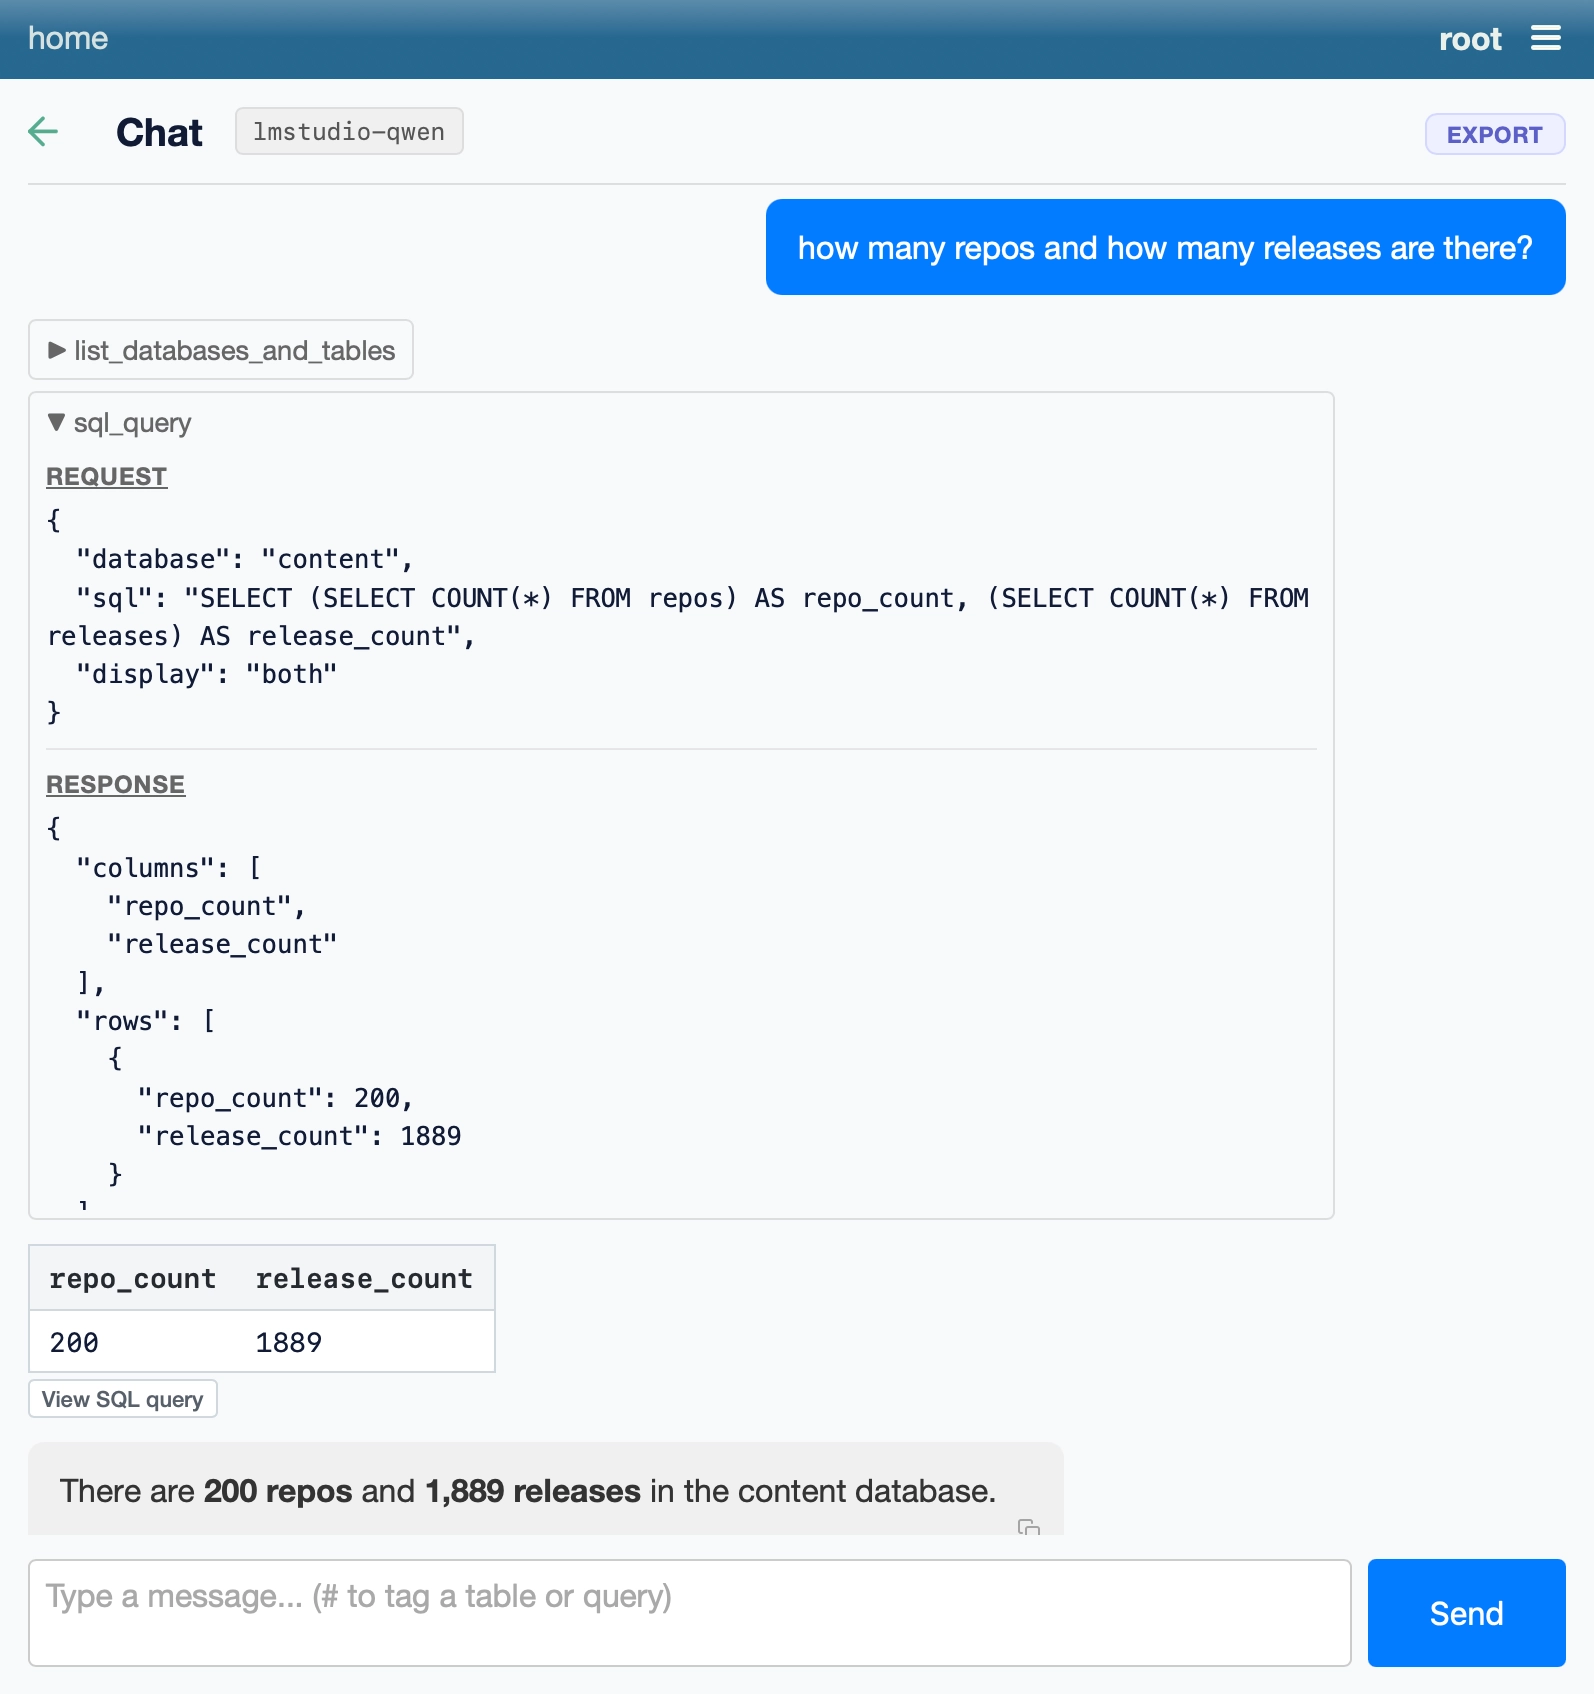
Release: datasette-agent 0.6a0 Accumulated small fixes for Datasette Agent, my agent plugin for Datasette that lets you ask questions about your data. Most notably, it now adds an agent prompt directly to the Datasette homepage, with...

OpenAIAI labs

Our new blog for science

The OpenAI science blog shares new findings, practical methods, and firsthand accounts from researchers using AI to advance scientific discovery.

Simon WillisonAI press

datasette 1.0a43

Release: datasette 1.0a43 I've been leaning hard into Claude Fable 5.2 to help knock things off the 1.0 milestone , which is now 53% complete. The biggest 1.0 item in this release is streaming support for output renderers - the built-in...

Simon WillisonAI press

datasette 0.65.6

Release: datasette 0.65.6 I backported a minor security fix from 1.0a43: Fixed a security issue where a database registered using add_database(db, name=..., route=...) with a route that differs from its name could be downloaded from /...

Simon WillisonAI press

datasette-apps 0.4a0

Release: datasette-apps 0.4a0 Datasette Apps are sandboxed HTML and JavaScript applications that live inside Datasette - think Claude Artifacts, but these ones can run SQL queries against your data. 0.4a0 adds support for linking: you...

Saturday, 14 November6 days ago

Simon WillisonAI press

datasette-llm 0.1a11

Release: datasette-llm 0.1a11 datasette-llm is the intermediate plugin for Datasette that supports configuring LLMs for use with other Datasette plugins. This release adds support for OpenAI-compatible endpoints, so you can configure...

Simon WillisonAI press

datasette-vega 0.7

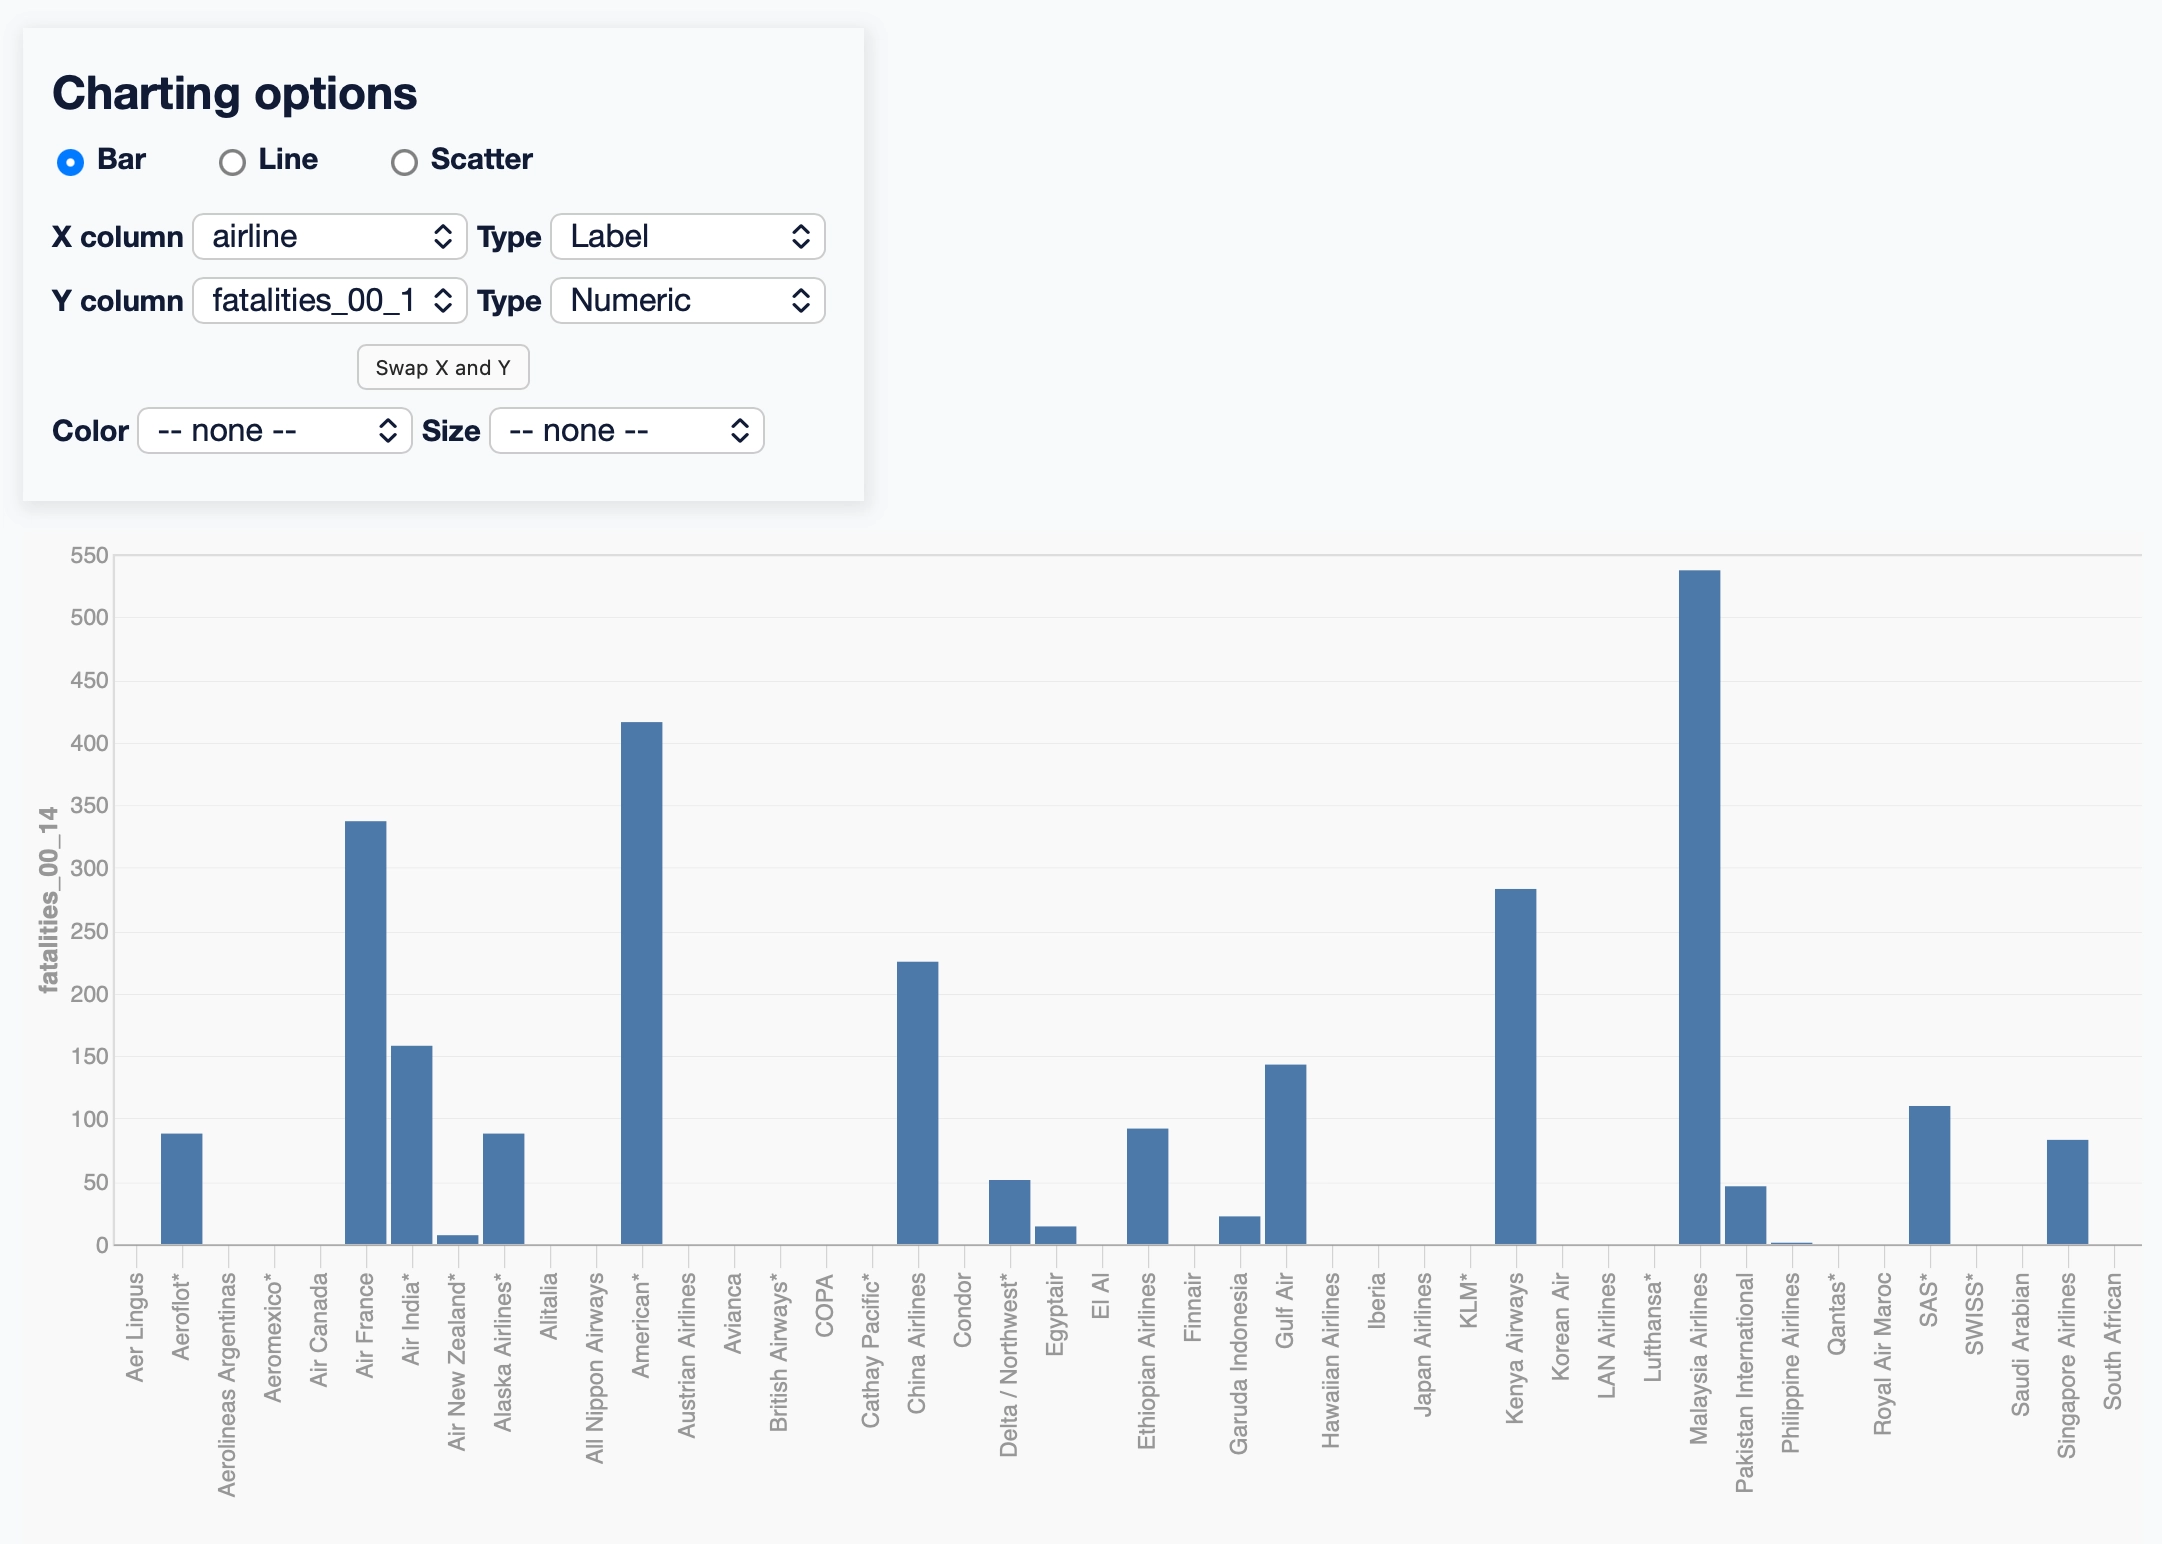
Release: datasette-vega 0.7 A new release of Datasette's longest untouched plugin, for rendering charts (using Vega-Lite ) against data in a table or custom query. The last release was in July 2018! I finally bumped it for compatibility...

Schneier on SecuritySecurity press

Upcoming Speaking Engagements

This is a current list of where and when I am scheduled to speak: I’m speaking at the Catalyst Summit in Brampton, Ontario, Canada, on Wednesday, November 18, 2026. I’m speaking at QT Qonference 2026 in Toronto, Ontario, Canada, on...