Hacks
81 articlesFriday, 30 Octobertoday
HackReadHacks
Binance Probes DevOps Engineer’s Hacked Laptop After $6.3B Theft
Binance probes a DevOps engineer’s hacked laptop after a $6.3 billion theft linked by researchers to North Korean hackers, and promises to cover all customer losses.

The Hacker NewsHacks
Official Claude Code VS Code Extension Compromised to Install Persistent SSH Backdoor
Cybersecurity researchers have disclosed that the official Anthropic Claude Code extension was compromised on the Open VSX registry to install a persistent SSH backdoor on infected hosts. The issue has since been traced to the...

The Hacker NewsHacks
Hackers Actively Exploit Highly Critical Drupal Commerce Core Authorization Bypass Flaw
Drupal has warned that threat actors are exploiting a "highly critical" security flaw in its Commerce Core component. The vulnerability, tracked as CVE-2026-118539 (CVSS score: N/A), is a case of missing authorization affecting Commerce...

The Hacker NewsHacks
CISA Adds Actively Exploited GitLab RCE and Cisco Firewall DoS Flaws to KEV
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Thursday added two security flaws impacting Cisco and GitLab software to its Known Exploited Vulnerabilities (KEV), citing evidence of active exploitation. The...
Security AffairsHacks
Hacker leaks data on more than 40,000 Homeland Security employees
A hacker leaks personal data on more than 40,000 DHS employees, including CBP, ICE and CISA staff, after an undisclosed breach. Personal details of thousands of U.S. Department of Homeland Security (DHS) employees are now online after a...

The Hacker NewsHacks
Binance Suffers Security Breach Affecting $6.3 Billion in Assets, Nearly $3 Billion Frozen
Cryptocurrency giant Binance said on Thursday that a "security incident" on its platform has impacted about $6.3 billion worth of assets. The world's biggest cryptocurrency exchange said nearly $3 billion of those assets have been...
HackReadHacks
Binance Probes Suspected $5.8 Billion Crypto Hack, $3 Billion Frozen
Binance investigates a $5.8 billion crypto theft, with $3 billion in assets frozen. The exchange says user funds are safe as investigators trace funds.
Thursday, 29 Octoberyesterday

Security AffairsHacks
Binance Investigates Suspicious Crypto Transfers Worth Up to $5.8 Billion
Binance probes suspicious crypto transfers worth up to $5.8 billion as Tether and Circle freeze $1.79 billion in stablecoins linked to the activity. Binance is investigating a potential security incident after billions of dollars in...

Security AffairsHacks
US Probes Suspected Hack Behind Military Base Freezer Failures
The Pentagon treats August freezer failures at US military bases as a suspected hack and is working with French investigators after a supermarket attack. The Pentagon is investigating freezer failures that spoiled food at US military...

The Hacker NewsHacks
ThreatsDay: Critical Firewall Flaws, Banking Trojans Rented, Weaponized PDF, Token Theft + 26 More Stories
Some attacks take real skill. Others just need someone to leave a door open. This week has both. Exposed passwords, old bugs still getting exploited, and trusted software doing things it shouldn't. There's a strange mix of clever tricks...

Security AffairsHacks
484,142 Exposed Cloud Buckets Contain 18 Billion Files
42 publicly listable cloud buckets containing 18 billion files, including exposed credentials, database dumps and backups. The Ransomnews research team counted 484,142 publicly listable cloud storage buckets in October 2026, holding...

Security AffairsHacks
U.S. CISA adds Linux Kernel and Broadcom VMWare ESX flaws to its Known Exploited Vulnerabilities catalog
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Linux Kernel and Broadcom VMWare ESX flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added Linux...
DataBreaches.netHacks
Extent of Crime Stoppers data breach unknown: Sault Police chief
James Hopkin reports: The Sault’s police chief says it’s currently unclear how many anonymous tips received by Crime Stoppers locally were potentially exposed in a massive data breach. Both the Sault Ste. Marie Police Service and the...
DataBreaches.netHacks
UNM Health addresses cyberattack in New Mexico after ransomware group claims responsibility
John Rupolo reports: University of New Mexico Health is addressing concerns after a cyberattack on Monday, with reports surfacing this week that a ransomware group claimed responsibility for the incident. “So what I can say is we’re...
DataBreaches.netHacks
Florida education department says data breach may affect 4.9 million people
Eric Weiss reports: The Florida Department of Education says a breach of its student financial aid website may have exposed personal information, including Social Security numbers, belonging to approximately 4.9 million people. The...
DataBreaches.netHacks
A RIZAP Employee Uploaded 726 People’s Health Records to a Personal AI Chat
Rowan Sterling reports: On 20 August 2026 an employee of RIZAP Inc., the Japanese fitness and health-guidance group, was pulling records out of the health-guidance management system it operates for insurers when the data went into a...
DataBreaches.netHacks
Australia severs criminal access to 180,000 computers after breaching Amadey malware backend
Lukas Brandt writes: Criminals using the Amadey malware lost control of about 180,000 infected computers after operators from the Australian Signals Directorate (ASD) gained access to the operation’s backend and severed the connection...
DataBreaches.netHacks
Student SSNs and Medicaid IDs Exposed in Frontline School Software Breach
Kalleigh Lane reports: If your school district used Frontline Central or School Health Management, your Social Security number, date of birth, or government ID could have been caught up in a cybersecurity incident. That risk applies to...
DataBreaches.netHacks
DHS personnel leak exposes contact details and sensitive job information
David DiMolfetta reports: Searchable records identifying more than 41,000 current and former Department of Homeland Security employees and contractors were published Wednesday, exposing contact information and details about sensitive...

The Hacker NewsHacks
Linux Kernel TCP Flaw With 9.8 CVSS Score Affects Ubuntu, Red Hat and Other Distributions
A flaw in the Linux kernel's TCP code, tracked as CVE-2026-98432, affects Ubuntu, Red Hat Enterprise Linux (RHEL), and other Linux distributions. The kernel's own CVE team rates it 9.8 out of 10 on the CVSS scale. Anthropic said on...
HackReadHacks
EMBRACE Flaws in 5 AI Coding Tools Enable Code Execution and File Theft
EMBRACE affects AI coding tools Cursor, GitHub Copilot, Codex, VS Code and Claude Desktop, enabling code execution, file theft and browser address-bar spoofing.

The Hacker NewsHacks
Fake ChatGPT and Claude Apps Abuse Signed Executables to Deploy Crypto Miners
Threat actors are delivering malicious loaders and cryptocurrency miners under the guise of artificial intelligence (AI) desktop applications for Anthropic Claude and OpenAI ChatGPT as part of a campaign dubbed Yoba. The activity...

The Hacker NewsHacks
Google's Gemini 4 Carbon Leads Benchmarks for Finding, Exploiting, and Patching Vulnerabilities
Google on Wednesday took the wraps off Gemini 4 Carbon, its latest frontier model with state-of-the-art cybersecurity and long-horizon capabilities. "It shows significant gains across coding and agentic tasks as well as across key...
HackReadHacks
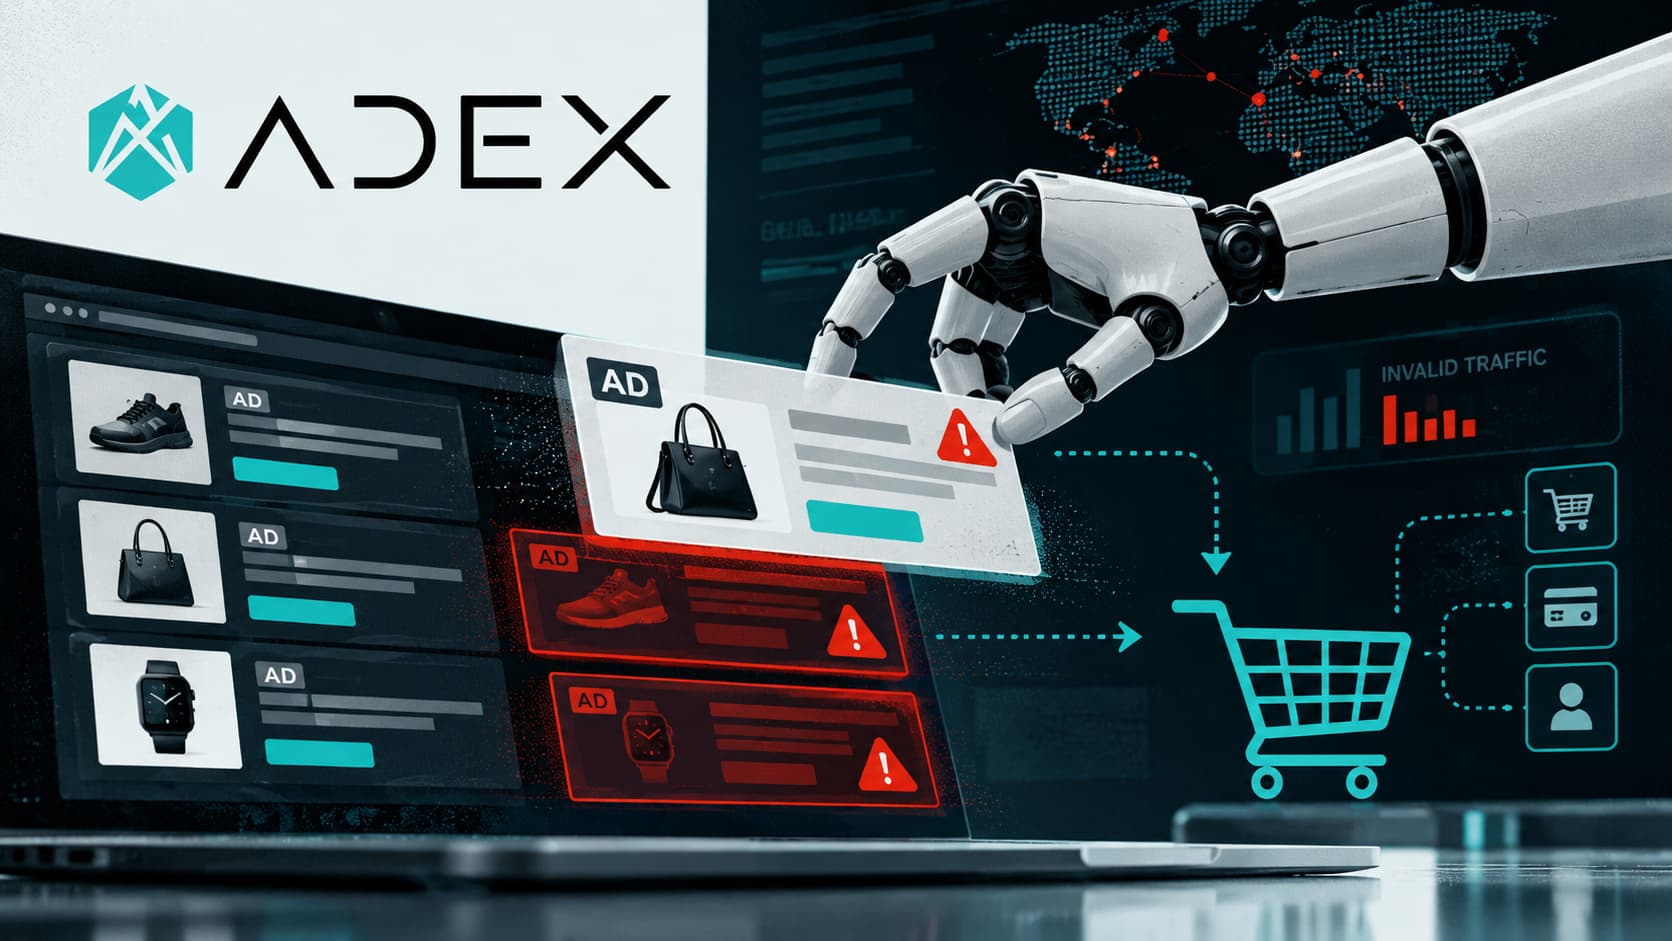
ADEX: AI Involved in 52% of Detected Ad Fraud Schemes – Shopping Agents Could be Next
New ADEX research shows how AI is making familiar scams cheaper and harder to detect, while fraudsters prepare to target AI shopping assistants.
HackReadHacks
AppViewX Expands Quantum Trust Hub with Cryptographic Discovery, Posture Management, and Remediation
New York, New York, 29th October 2026, CyberNewswire
HackReadHacks
Ukrainian Nefilim and Hive Affiliate Artem Stryzhak Jailed for 70 Months
Artem Stryzhak gets 70 months for Nefilim and Hive ransomware attacks targeting hospitals, government agencies and businesses in the US and overseas.

The Hacker NewsHacks
Webinar: How to Build AI Threat Readiness Into Your Security Operations
Security teams have spent years trying to detect threats faster. AI is changing the harder part: how much time defenders have left to act. Advanced AI models can now help attackers discover vulnerabilities, generate exploit code, and...

The Hacker NewsHacks
Telegram Android Flaw Lets Attackers Run Code When Users Answer Voice Calls
A flaw in Telegram for Android could be chained with two other bugs to take full control of a victim's phone through a voice call, once the victim answered, according to security startup NebuSec. The attacker needed only an ordinary...

The Hacker NewsHacks
The Rise of the Threat Operator: How AI Will Redefine Security Operations and Careers
AI is beginning to take over much of the work that has traditionally defined the security analyst's job. Investigating alerts, collecting evidence, correlating activity across tools, and executing response actions are becoming tasks...

The Hacker NewsHacks
26,400 Valid Cloud and AI Credentials Found Exposed in Public Gitee Repositories
26,400 credentials that developers left in public code on Gitee, a Chinese code-hosting service, still worked when a researcher tested them. Anyone who copied one from that code could have used it. Independent researcher Ben Zimmermann...

The Hacker NewsHacks
Cisco Patches Actively Exploited ASA and FTD VPN Flaw That Can Crash Firewalls
Cisco has released patches to address a high-severity security flaw in Secure Firewall Adaptive Security Appliance (ASA) Software and Secure Firewall Threat Defense (FTD) Software that it said has been exploited in the wild. The...

Security AffairsHacks
Volt Typhoon Used Silent Train to Hide Zero-Day Attacks
Volt Typhoon used disposable relay chains to hide zero-day attacks on critical systems. Lumen linked Silent Train to at least four zero-days. Lumen’s Black Lotus Labs has spent three years tracking a covert network it calls Silent...

The Hacker NewsHacks
GitHub Launches npm Firewall to Block Malicious Packages Before Installation
GitHub has announced that it's introducing a new package firewall as a preview to block installation of suspicious npm packages during installation time. "The firewall inspects both metadata requests and package downloads for signs of...

Security AffairsHacks
Election Website Security: 42% of US County Sites Still Lack .gov Domains
US election websites show improved security, but weak email protection, non-.gov domains and third-party tracking still expose voters to risks. Millions of Americans will use websites to check their registration, find polling places or...

The Hacker NewsHacks
Attacker Tried to Exploit Alpine Linux’s GitLab via CVSS 10.0 Flaw Its Ruby Left Open
An attacker tried to exploit a critical GitLab vulnerability on the Alpine Linux project's own GitLab server a week after GitLab released a fix, Alpine Linux said on 28 October. The flaw, CVE-2026-97229 (CVSS score: 10.0), can let an...

Security AffairsHacks
ENGIE Data Breach Exposes Customer Details and Energy Contracts
ENGIE says attackers accessed French customers’ contact and energy contract data through a partner sales tool. Banking data was not affected. French multinational energy company ENGIE warned customers in France that attackers accessed...
Security AffairsHacks
Virtualine Domain Seized, but Allegedly Abusive Website Remains Online
The FBI seized Virtualine, a hosting service accused of supporting criminal sites, ignoring abuse reports and helping launder money from illegal activities The FBI seized the website of Virtualine, a hosting service that sold its...

The Hacker NewsHacks
Hackers Exploited Cisco SD-WAN Flaw to Plant Malware Built to Steal Encryption Keys
Hackers exploited a critical Cisco Catalyst SD-WAN flaw, fixed in February, to plant custom malware inside the systems that control an organization's SD-WAN network. The malware, called KeyDrift, is designed to copy the keys that...

The Hacker NewsHacks
China-Linked Hackers Exploited VMware ESX Zero-Day to Reduce Audit Trail Visibility
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Wednesday added a security flaw impacting Broadcom VMware ESX to its Known Exploited Vulnerabilities (KEV) catalog, after CrowdStrike revealed that it had been...

The Hacker NewsHacks
Attackers Exploit PHP2Shell Flaws in Internet-Exposed Palo Alto Networks Management Interfaces
Palo Alto Networks on Wednesday warned that threat actors are exploiting the recently patched PHP2Shell vulnerabilities against publicly-accessible management interfaces. "Active exploitation has been observed targeting the Palo Alto...
HackReadHacks
Transferring Unused IPv4 Addresses in Asia Pacific: The Complete APNIC Playbook
Understand APNIC IPv4 transfer rules, buyer requirements, fees and approval steps, with helpful checks to assess address blocks before completing a transaction.
Wednesday, 28 October2 days ago
HackReadHacks
Next-gen privacy protocols: WireGuard vs OpenVPN vs Shadowsocks
Compare WireGuard, OpenVPN and Shadowsocks for speed, privacy, enterprise access and censorship resistance, including VPN tunnels differ from encrypted proxies.
Security AffairsHacks
Hive and Nefilim Ransomware Affiliate Gets 70 Months In Jail
Artem Stryzhak gets 70 months in prison for Hive and Nefilim ransomware attacks, while the FBI offers $11 million for his alleged co-conspirator. A federal court in Brooklyn has sentenced Artem Stryzhak, a Ukrainian national, to 70...
HackReadHacks
From Rules to AI and Back
Fraud prevention combines rules, AI and behavioral analytics to stop scams, reduce false declines and keep automated decisions explainable through human review.

The Hacker NewsHacks
Volt Typhoon Used Covert Silent Train Network in Four Zero-Day Exploitation Campaigns
The China-nexus cyber espionage group known as Volt Typhoon has been attributed to a now-disrupted covert access network dubbed Silent Train that has been put to use for zero-day exploitation and strategic access. "First identified in...
HackReadHacks
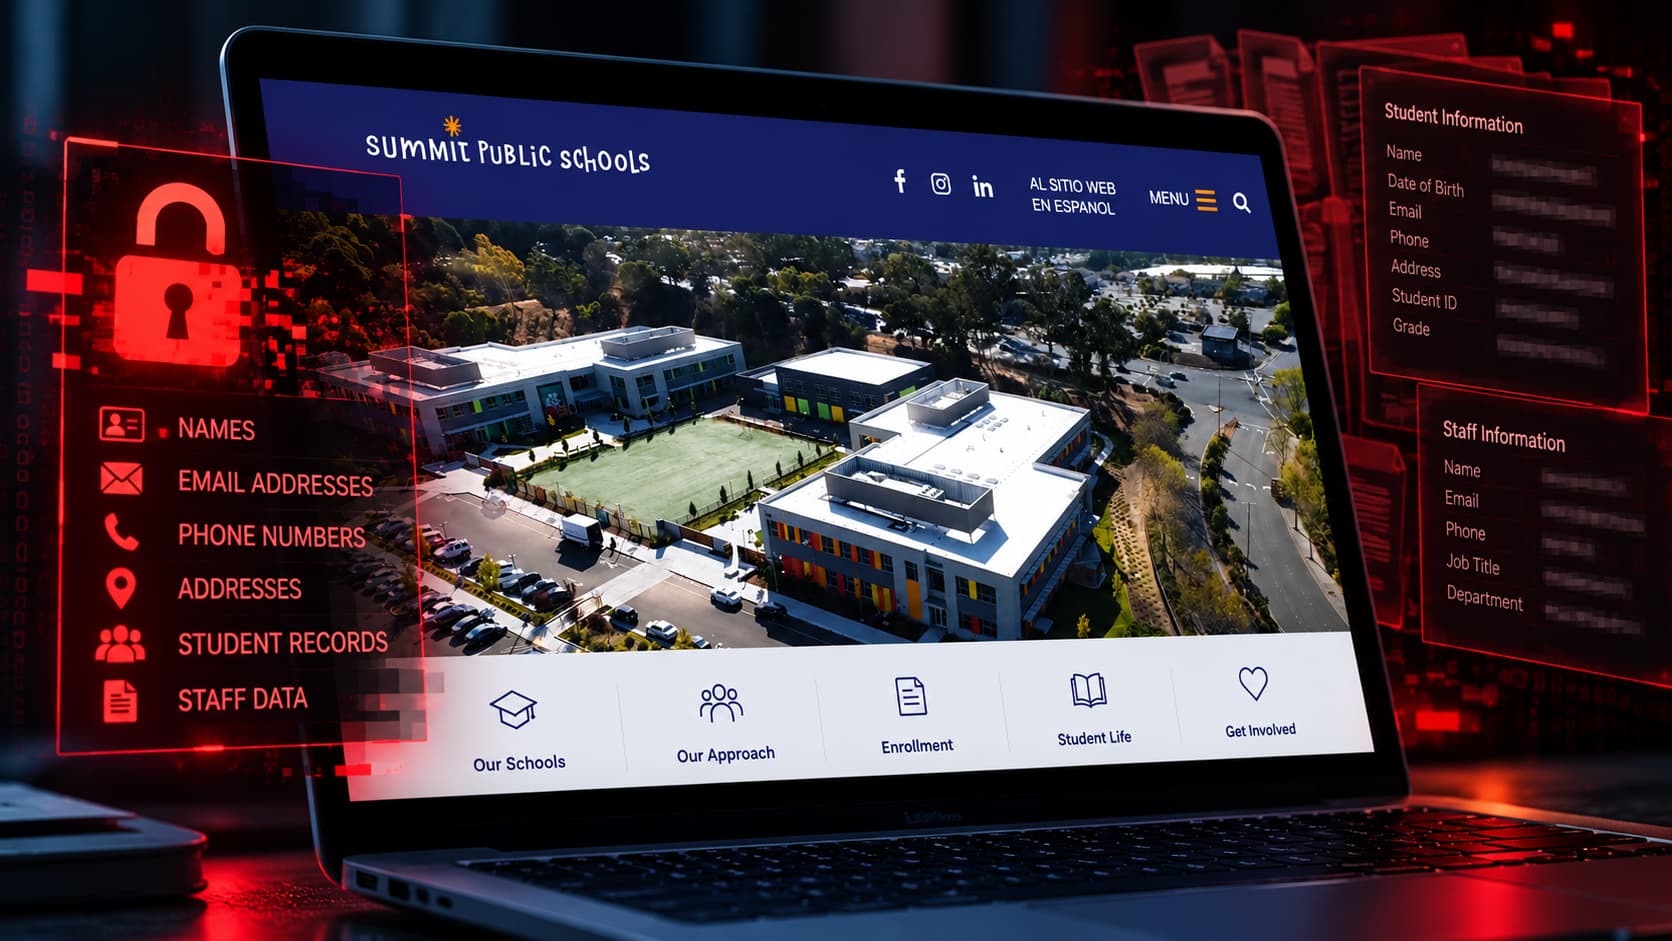
Summit Public Schools Breach Exposes 115 GB of Student and Staff Data
A hacker has leaked 115 GB of Summit Public Schools data containing billions of lines, student and staff…
HackReadHacks
OffSec Launches Free PHP2Shell Lab Following Critical Vulnerability Discovery
New York, United States, 28th October 2026, CyberNewswire

The Hacker NewsHacks
Google to Allow One-Tap Android App Installs From Approved Third-Party Stores Outside U.S.
Third-party Android app stores can now apply to Google for permission to install apps with one tap, without Android's usual confirmation screens, and to update them in the background. To qualify, a store must pass identity checks and...

The Hacker NewsHacks
Researcher Reveals How Logic Bugs Alone Cracked Microsoft Edge in $175,000 Pwn2Own Win
A chain of logic flaws, with no memory corruption, can turn a malicious web page into code running on a Windows computer outside Microsoft Edge's sandbox, a security researcher has shown. Orange Tsai of DEVCORE published the full method...

The Hacker NewsHacks
PHP2Shell Attack Roots 25 Servers, Breaches U.S. Government-Affiliated Network
Cybersecurity researchers have disclosed details of what appears to be an artificial intelligence (AI)-assisted attack orchestrated by a suspected China-nexus threat actor that has leveraged the PHP2Shell vulnerabilities to breach...
DataBreaches.netHacks
JPN: Times Car reporting ¥5.5 billion loss has firms bracing for data breach fallout
Maddie Baker and Spencer Landers As cyberattacks continue across Japan, companies are coming to realize the great financial risk of such attacks if their lax cybersecurity systems cause millions of peoples’ personal information to be...

The Hacker NewsHacks
Hackers Target Critical Oracle E-Business Suite RCE Flaw Days After Security Patch
Threat actors are beginning to probe for a newly patched critical vulnerability in Oracle E-Business Suite (EBS), according to threat intelligence firm Defused Cyber. The vulnerability in question is CVE-2026-101767 (CVSS score: 9.8) ,...
DataBreaches.netHacks
KR: Bithumb discloses data leak after internal system breach; One of three financial firm breaches reported that day
CoinTelegraph reports: South Korea’s crypto exchange Bithumb is investigating the extent of a data leak caused by a hack of its internal mobile system earlier this week, Yonhap News Agency reported Wednesday. Bithumb discovered the...
DataBreaches.netHacks
Japanese internet giant GMO tells customers to shut down and disconnect PCs from the internet following data breach and ransomware threat
Sead Fadilpašić reports: Japanese internet giant GMO Group has told its customers to scan their computers for viruses, back up all of their data, disconnect the devices from the internet and then shut them down. The announcement, which...

The Hacker NewsHacks
Critical 16-Year-Old UEFI Flaw Can Run Code Before Secure Boot on Network-Booting Servers
A critical 16-year-old flaw in EDK II, the open-source code that most hardware makers use to build UEFI firmware, can allow an attacker to run code on a machine before its operating system loads, but only while the machine is booting...

The Hacker NewsHacks
Wazuh and AI for Enhanced SOC Workflows
Artificial Intelligence (AI) has become one of this decade's defining technologies. From healthcare and finance to manufacturing and education, organizations increasingly rely on AI to automate repetitive tasks, uncover patterns hidden...

The Hacker NewsHacks
Adobe Fixes 8 Critical Campaign Classic Flaws Allowing Code Execution and Security Bypass
Adobe has released patches to address multiple critical security flaws in Campaign Classic that, if successfully exploited, could result in arbitrary code execution, security feature bypass, and privilege escalation. The list of eight...

The Hacker NewsHacks
American Organizations Under Attack: Skyw4lker Device Code Phishing Campaign Exposed
Modern phishing campaigns can compromise American businesses without relying on traditional credential theft. Attackers can abuse legitimate cloud services, authentication mechanisms, and trusted business workflows to gain access to...

The Hacker NewsHacks
Anthropic's Unreleased AI Model Chains Flaws Into Working Chrome, Safari, Windows and Linux Exploits
An unreleased Anthropic AI model found security flaws in Chrome, Safari, Android, Windows, and Linux and chained them into working proof-of-concept exploits, the company said in its latest report. The exploits were built in the lab...

The Hacker NewsHacks
FBI Seizes Virtualine Domain Over Alleged Criminal Hosting and Bitcoin Money Laundering
The U.S. Department of Justice (DoJ) on Tuesday announced the seizure of a domain associated with a bulletproof hosting provider (BPH) named Virtualine. The move was in response to the service being used to commit and facilitate...

The Hacker NewsHacks
Japan's GMO Offers $1 Million Bounty to Catch Hackers Behind FX Trading Cloud Breach
Japan's GMO Internet Group is offering up to $1 million in total for tips that help catch the attackers who breached its Onamae.com Desktop Cloud service, after refusing to pay an extortion demand. The reward program opened on October...

The Hacker NewsHacks
Tailscale Patches SSH Flaws That Could Let Hacked Devices Gain Root Access on Other Servers
Tailscale has released version 1.104.4 to fix flaws in its built-in SSH server that could let an attacker reach services and files on other servers that only the root user should be able to touch. The flaws are in how Tailscale SSH...

The Hacker NewsHacks
ShinyHunters-Exploited Oracle PeopleSoft Zero-Day Turns Out to Be Three Chained Flaws
The critical Oracle PeopleSoft bug that ShinyHunters has exploited since May is not one flaw but three chained together, the researchers who reported it said this week. Oracle patched all three under a single identifier, CVE-2026-35273,...

The Hacker NewsHacks
Adobe Commerce PolyShell Attacks Breach Hundreds of Stores as Brotli Exploit Traffic Emerges
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Tuesday added two vulnerabilities impacting Adobe Commerce and Magento, and Google's Brotli decoder library to its Known Exploited Vulnerabilities (KEV) catalog, citing...
Tuesday, 27 October3 days ago

The Hacker NewsHacks
CyberStrikeAI Uses 44 AI Agents to Automate Hacking Operations Against Japan Targets
Cybersecurity researchers have disclosed details of three cyber attacks targeting organizations in Japan in which artificial intelligence (AI) was a key element, either in the driving seat or to assist a human operator. TrendAI, which...

The Hacker NewsHacks
GoAhead TLS Flaws Allow Revoked Client Certificates and Enable Session Decryption
The GoAhead embedded web server loaded a certificate revocation list into its default TLS backend but never turned revocation checking on, so a revoked client certificate could still pass login on affected setups. The flaw is in builds...

The Hacker NewsHacks
Apple Backports Fix for Exploited CoreGraphics Flaw to Older iPhones and iPads
Apple on Monday backported fixes for a high-severity security flaw that was exploited in real-world cyber attacks to older devices. The vulnerability, tracked as CVE-2026-86950 (CVSS score: 8.8), is an out-of-bounds write affecting...

The Hacker NewsHacks
Microsoft Authenticator Flaw Let Permissionless Android Apps Steal Work Account Tokens
Microsoft has fixed a flaw in its Authenticator app for Android that let a malicious app with no permissions pose as a trusted Microsoft app, such as Teams, and collect sign-in tokens for a victim's work account. Microsoft tracks the...

The Hacker NewsHacks
Keystone to Destroy 18,835 Hardware Wallets After Hackers Steal Device Verification Key
An attacker who gained access to Keystone's website obtained the key that its hardware wallets use to prove they are genuine, the company said in a statement on October 26. Someone with that key could build counterfeit devices that pass...

The Hacker NewsHacks
AI-Generated Fake Login Pages Are Making Account Takeovers Easier
Fake login pages are nothing new, but generative AI is making them easier to build and more convincing. Attackers can recreate familiar login screens, impersonate trusted brands and tailor phishing attempts to specific employees or...

The Hacker NewsHacks
Lazarus Abuses South Korean Security Software to Deploy Malware Using Post-Quantum Encryption
The North Korea-linked Lazarus Group has been attributed to a cyber espionage campaign dubbed Operation FlashHole targeting at least three organizations in South Korea spanning the construction, software, and wire-communication...

The Hacker NewsHacks
Australia Gets Into Amadey Malware Backend, Cuts Off Access to 180,000 Infected Computers
A criminal using the Amadey malware can no longer access or steal data from 180,000 infected computers around the world, including some in Australia, the Australian Signals Directorate (ASD) says. The agency's operators gained access to...

The Hacker NewsHacks
OpenAI Compaction Flaw Let Researchers Bypass Hidden Reasoning Protections
OpenAI's compaction feature, which shrinks a long conversation to save space, could be turned into a way to copy a model's hidden reasoning out in plain text, security firm Xint has shown. OpenAI's reasoning models work through a...

The Hacker NewsHacks
Attackers Hijack Dahua IP Cameras in Ukraine Using P2P Access and Auth Weaknesses
The Computer Emergency Response Team of Ukraine (CERT-UA) has issued an alert warning of unauthorized remote access to video surveillance systems manufactured by Dahua. "Cases of compromising IP cameras and DVRs with access to the video...

The Hacker NewsHacks
CISA Confirms Active Exploitation of Two PHP2Shell Flaws Enabling Remote Code Execution
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Monday confirmed active exploitation of the recently patched PHP2Shell flaws by adding them to its Known Exploited Vulnerabilities (KEV) catalog. The PHP...
Monday, 26 October4 days ago

The Hacker NewsHacks
Hackers Infect 953 Online Stores With Scanner-Evading JavaScript, Mostly on Magento
An unknown threat actor has infected 953 online stores, most of them running Magento, as part of a long-running campaign active since July 2025. According to Dutch e-commerce security company Sansec, the activity is designed to add a...

The Hacker NewsHacks
PHP Issues Second Windows Security Update in Five Days to Fix Brotli Code Execution Flaw
PHP has rebuilt its official Windows packages for PHP 8.2 through 8.5 to fix CVE-2026-111497, a flaw in the Brotli compression library that the packages include. The flaw can let an attacker corrupt memory and potentially run code. PHP...

The Hacker NewsHacks
Attackers Use Microsoft Teams IT Support Scams to Deploy Malware and Ransomware
Cybersecurity researchers are calling attention to what they say is a "recurring social engineering pattern" across hundreds of cases in which threat actors use Microsoft Teams' external chat creation feature to conduct impersonation...

The Hacker NewsHacks
⚡ Weekly Recap: This2Shell, That2Shell, Everything's an RCE? Rogue AI, Supply Chain Chaos and More
This2Shell, That2Shell, Everything2Shell. That's pretty much how the last week went. Critical bugs that let attackers run code remotely are showing up everywhere. Hackers are scanning for targets, some flaws are already being used in...

The Hacker NewsHacks
Two Critical Wasmtime Flaws Could Let Malicious WebAssembly Modules Escape Sandboxes
Two critical flaws in Wasmtime, a WebAssembly runtime that can be built into other software, could allow a malicious WebAssembly module to escape the sandbox intended to contain it, the project's maintainers say. An attacker would first...
