Security press
119 articlesFriday, 30 Octobertoday
The RecordSecurity press
Polymarket confirms cyberattack on third-party provider after outages
The company suffered outages starting at 2pm EST on Thursday and eventually attributed the downtime to a compromise involving an unnamed provider.

The RecordSecurity press
Russian popular home goods chain faces days of disruption following cyberattack
Poryadok, which operates 48 stores across 32 Russian cities, first reported technical problems on Sunday, saying its website, mobile app and physical stores were temporarily unavailable.
BleepingComputerSecurity press
Microsoft finally fixes VPN issues caused by September updates
Microsoft has resolved Always On VPN connection failures triggered after installing the September 2026 Windows 11 security updates. [...]

SecurityWeekSecurity press
Drupal Commerce Core Vulnerability Exploited Against Online Stores
Drupal says a highly critical Commerce Core access bypass is exploited in the wild and urges store owners to audit their orders. The post Drupal Commerce Core Vulnerability Exploited Against Online Stores appeared first on SecurityWeek .

BleepingComputerSecurity press
Drupal warns of critical Commerce Core flaw exploited in attacks
Drupal warned admins to patch a critical access bypass vulnerability in the Commerce Core module that attackers are exploiting in the wild. [...]

SecurityWeekSecurity press
$2 Million+ Drained From Polymarket Traders in New Supply Chain Attack
Malicious code linked to a website monitoring tool was designed to hijack logged-in Polymarket sessions and siphon user funds. The post $2 Million+ Drained From Polymarket Traders in New Supply Chain Attack appeared first on SecurityWeek .

SecurityWeekSecurity press
Max-Severity GitLab Vulnerability Exploited Against Alpine Linux
Tracked as CVE-2026-97229, the bug allows unauthenticated attackers to execute arbitrary code on the server. The post Max-Severity GitLab Vulnerability Exploited Against Alpine Linux appeared first on SecurityWeek .

BleepingComputerSecurity press
Binance links $6.3 billion crypto theft to compromised DevOps laptop
Binance, the world's largest crypto exchange, has linked the theft of about $6.3 billion in cryptocurrency to a DevOps engineer's compromised laptop. [...]

SecurityWeekSecurity press
TeamViewer Flaw Could Let Malicious Hosts Take Over Support Technicians’ Machines
An integer overflow tracked as CVE-2026-111585 could be used to execute arbitrary code on the viewer’s system. The post TeamViewer Flaw Could Let Malicious Hosts Take Over Support Technicians’ Machines appeared first on SecurityWeek .

SecurityWeekSecurity press
$6 Billion Binance Hack Bears Hallmarks of North Korea’s TraderTraitor
Blockchain analysts link the record crypto theft to North Korean hackers, as Binance probes a possibly compromised engineer laptop. The post $6 Billion Binance Hack Bears Hallmarks of North Korea’s TraderTraitor appeared first on...
Dark ReadingSecurity press
As Russia's Cyberwar Evolves, Belarus Steps Forward
The "FrostyNeighbor" advanced persistent threat (APT) launched a destructive attack in Ukraine and is raising concerns about deeper alignment with Russian cyber objectives.
The RecordSecurity press
Binance hit by record $6.3 billion crypto hack, scrambles to freeze funds
Binance, the world's largest cryptocurrency exchange, confirmed Thursday that it had been hacked in a $6.3 billion cyber heist that blockchain investigators are blaming on North Korea.
Thursday, 29 Octoberyesterday
BleepingComputerSecurity press
OpenAI doubles ChatGPT Pro usage limits after backlash over planned 50% cut
OpenAI says it won't reduce usage limits for the $100, $200, and $500 ChatGPT Pro plans, as well as Business Premium, and it also promised to keep Dots usage independent. [...]

BleepingComputerSecurity press
Binance probes potential $5.8 billion crypto-theft hack
Cryptocurrency exchange Binance is investigating a potential security breach involving up to $5.8 billion in digital assets, in what could become the largest cryptocurrency hack in history. [...]

BleepingComputerSecurity press
Hugging Face malware campaign returns to hijack GPUs for crypto mining
A crypto-mining campaign abusing Hugging Face models returned days after takedown, hijacking GPU servers and planting backdoors, with one model downloaded over 28,000 times. Separately, a fake Solana starter kit on GitHub is positioned...

BleepingComputerSecurity press
Japan Airlines suffers third-party data breach exposing passenger info
Japan Airlines (JAL) has announced that a data breach at Amadeus's Passenger Service System exposed the data of about 92,000 customers. [...]

BleepingComputerSecurity press
Polymarket halts trading after crypto-draining script breach, $2.5M traced
Prediction market platform Polymarket temporarily suspended trading on Thursday after hackers compromised a third-party service to distribute cryptocurrency-draining JavaScript, with approximately $2.5 million in assets traced to a...
Dark ReadingSecurity press
Anthropic-Themed Phishing Emails Bypass Top Security Tools
Obvious phishing emails with numerous red flags are somehow getting past some of the industry-leading secure email gateway (SEG) products.
Dark ReadingSecurity press
Rethinking Cybersecurity Awareness in the AI Era
This installment of the Reporters' Notebook video series discusses some of the trends and topics from Cybersecurity Awareness Month, from using AI for better training to educating next-generation workforces on modern risks and emerging...
The RecordSecurity press
Limited reports of PHP bug exploitation emerge
One cyber firm listed a half-dozen exploitations of the PHP2Shell bugs, and another identified a well targeted, suspected Chinese campaign that breached U.S. "government affiliated" servers.
The RecordSecurity press
GM settles with 36 states for selling driver data, agrees to $220 million fine and reforms
General Motors agreed to pay $220 million to settle a lawsuit filed by a coalition of 36 state attorneys general who alleged the company unlawfully sold information about driver behavior to outside parties.

BleepingComputerSecurity press
Fake crypto app on Apple App Store linked to $23K wallet theft
A fake cryptocurrency trading app called Padre Terminal, previously available on the Apple App Store for iOS devices, has been linked to the theft of approximately $23,000 from 27 Solana wallets. [...]

BleepingComputerSecurity press
Hackers exploit Cisco SD-WAN flaw to deploy custom KeyDrift malware
A newly identified advanced persistent threat (APT) group tracked as UAT-11473 was observed exploiting CVE-2026-20127, an authentication-bypass flaw in Cisco Catalyst SD-WAN Controllers, to deploy a custom malware framework called...
Dark ReadingSecurity press
Claude Model Builds Exploits Across Major Browsers & OSes
An unreleased version of the AI model has found and chained multiple vulnerabilities in Chrome, Safari, Android, Windows, and Linux, Anthropic says.

SecurityWeekSecurity press
When Risk Becomes Personal: What Security Leaders Can Learn From a Cancer Diagnosis
Risk managers are trained to spot weak signals, plan for disruption and make hard decisions under uncertainty. But the discipline looks different when the risk is not a system or an enterprise, but you. The post When Risk Becomes...
The RecordSecurity press
Federal bankruptcy courts contractor says no data stolen during cyber intrusion
"No data was extracted,” a spokesperson for BAE Systems, a federal contractor, told Recorded Future News about its probe into a cyberattack against its systems for federal bankruptcy courts.

BleepingComputerSecurity press
Chrome extensions with 13.4 million installs caught hijacking searches
A massive search-hijacking campaign involving 319 Chrome extensions with a combined 13.4 million reported installations redirected users' searches through tracking servers to generate advertising revenue from Bing and Yahoo. [...]
Dark ReadingSecurity press
Threat Modeling With 4 Simple Questions on a White Board
A four-question exercise that CISOs can use to create a threat model that promises results, without a big spend.

SecurityWeekSecurity press
Google Touts Powerful Cybersecurity Capabilities in Gemini 4 Carbon Model
Google’s new frontier model scored 88.2% on SEC-bench Pro and is rolling out first to vetted cyber defenders via its Fairwind Program. The post Google Touts Powerful Cybersecurity Capabilities in Gemini 4 Carbon Model appeared first on...

SecurityWeekSecurity press
How Secure Are US Elections? Voting Machine Risks and the Growing Threat of AI
Unpatched voting machines, unverifiable QR-coded ballots, and AI-driven influence campaigns leave US elections short of secure. The post How Secure Are US Elections? Voting Machine Risks and the Growing Threat of AI appeared first on...
BleepingComputerSecurity press
Microsoft fixes Remote Desktop failures caused by recent Windows updates
Microsoft has resolved a known issue that prevents non-admin users from connecting to devices via Remote Desktop when the "Administrator protection" security feature is enabled. [...]

SecurityWeekSecurity press
Cisco Open Sources Quarry to Catch AI Agent Attacks Hidden in Harmless Steps
Cisco open sourced Project Quarry, a rule language for detecting AI agent attacks that only emerge across sequences of benign actions. The post Cisco Open Sources Quarry to Catch AI Agent Attacks Hidden in Harmless Steps appeared first...
BleepingComputerSecurity press
3 Ways AI Agents Already Operate in Your Browser
AI agents can control authenticated browsers, interact with corporate applications, and access sensitive data while appearing to act as legitimate employees. Keep Aware examines three ways agents operate inside browsers and why...

BleepingComputerSecurity press
CISA warns of Fragnesia Linux flaw chained in PHP2Shell attacks
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) warned federal agencies to patch a high-severity Linux kernel privilege escalation bug that attackers are chaining with the PHP2Shell flaws in the wild. [...]
The RecordSecurity press
FTC to probe major companies over personalized pricing and pay
The Federal Trade Commission ordered nine food delivery, airline and ride-sharing companies to turn over detailed information on how they harness personal data to set individual consumer prices and employee compensation.

SecurityWeekSecurity press
Adobe, Veeam, Juniper Networks Patch Critical Vulnerabilities
The flaws could lead to arbitrary code execution, authorization bypasses, and privilege escalation. The post Adobe, Veeam, Juniper Networks Patch Critical Vulnerabilities appeared first on SecurityWeek .
Ars Technica securitySecurity press
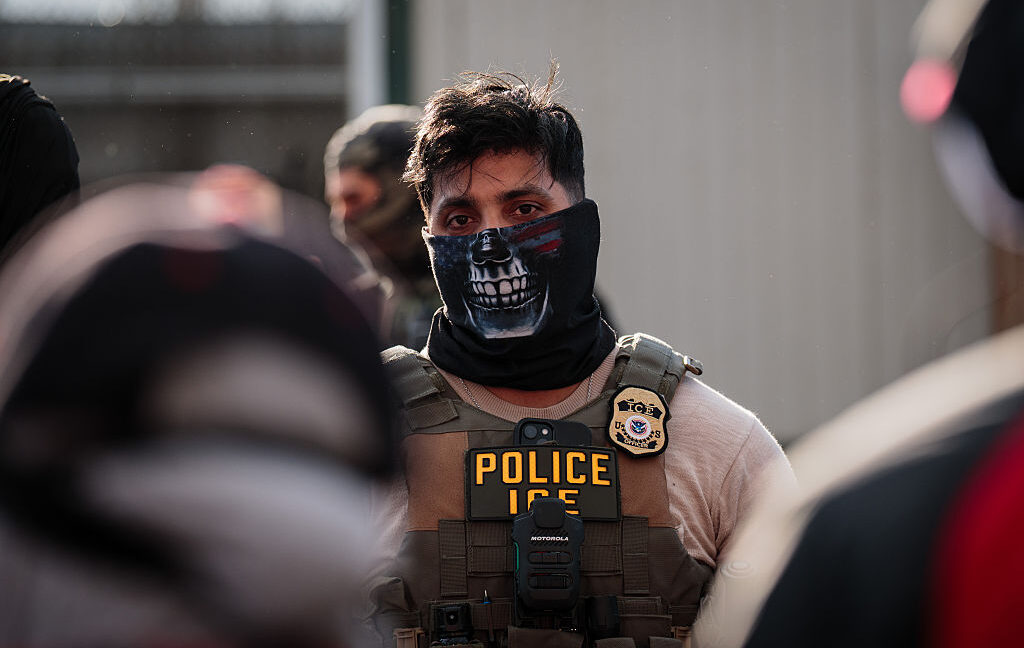
Massive leak exposes 41,000 DHS workers and undercover ICE agents
The leak reveals undercover agents, surveillance groups, and sensitive DHS access.
BleepingComputerSecurity press
Windows 11 KB5127936 update released with 41 changes and fixes
Microsoft released the KB5127936 preview cumulative update for Windows 11 versions 25H2 and 26H2, with 41 changes, including File Explorer and Cloud rebuild improvements. [...]

BleepingComputerSecurity press
New Cisco firewall zero-day exploited to crash SSL VPN devices
Cisco released security updates to patch a denial-of-service zero-day in Adaptive Security Appliance (ASA) and Threat Defense (FTD) software that attackers are exploiting to remotely crash vulnerable firewall devices. [...]
Dark ReadingSecurity press
Shadowy AI Relay Disables OpenAI Codex, Claude Code Sandboxes
The enigmatic service is providing popular AI coding tools to mainland China and other regions where OpenAI and Anthropic products are not officially for sale — but with key security features turned off.

Dark ReadingSecurity press
Cyber Vulnerabilities Besiege Italy, Absent Clear Cause
Researchers can't quite explain why cyber threats look so different in Italy compared with everywhere else.
Wednesday, 28 October2 days ago
Dark ReadingSecurity press
GhostAction Hacking Wave Fizzles, but Attackers Lurk on in GitHub
The supply chain attack campaign's shift toward developer endpoints and cloud access signals what could be next for the cybercrime outfit.
Dark ReadingSecurity press
AI Takes Root in Hospital Corridors, Raises Security Stakes
Artificial intelligence (AI) is everywhere in healthcare, from doctors’ intake forms to cancer screenings. But in some cases, life-and-death uses are outpacing cybersecurity.
Dark ReadingSecurity press
Attacker Relentlessly Scans for Credentials by Impersonating AI Bots
The threat actor lurked behind bots posing as agents from OpenAI, Anthropic, Meta, and others to find exposed data.
Dark ReadingSecurity press
Third Serengeti Sweep Tops 1,400 Arrests as Investigations Mature
Interpol's annual Operation Serengeti, now in its third iteration, led to 1,462 arrests across 20 African countries and the US, recovering $105 million in stolen funds.
Schneier on SecuritySecurity press
Studying Fraudulent North Korean IT Workers
Researchers set up a fake start-up company to study fraudulent North Korean IT workers.
Tuesday, 27 October3 days ago
Dark ReadingSecurity press
3 Frameworks to Protect CISOs & Orgs Against AI Liability
Cyber leaders can get ahead of AI liability with rigorous documentation, transparency, and smart contract negotiations with AI vendors.
Dark ReadingSecurity press
External Teams Chats Anchor 15-Minute Malware Delivery
Mail bombing is getting a new look with a wide-scale, ongoing social engineering campaign that might be tied to the Black Basta ransomware gang.

Ars Technica securitySecurity press
Code-execution flaw in UEFI firmware affects most servers on planet Earth
Critical flaw in EDK2 allows attackers to execute code early in the boot process.
Dark ReadingSecurity press
SBOMs Alone Can't Reveal the Scope of a Supply Chain Attack
A recent Shai-Hulud attack shows defenders need real-time visibility into production code and affected services to respond to supply chain compromises.
Dark ReadingSecurity press
Beware the Slasher: AI Could Kill Off Cybersecurity Pros' Skills
Nathan Hamiel outlines potential SecOps horror in the AI midst, as core technical capabilities go the way of reading an atlas or remembering phone numbers.
Dark ReadingSecurity press
'Aokigahara' Stealer Targets 'Developer Keyrings' & AI Assistants
The malware's focus on AI tools expands the traditional infostealer playbook to expose a forest of AI sessions, sensitive business data, and developer infrastructure from a single compromised endpoint.
Schneier on SecuritySecurity press
Hiding Capabilities in AI Models
Interesting research: “ AI Models Can Provably Hide Arbitrary Capabilities ” Abstract: Capability evaluations aim to surface dangerous model behaviors before deployment, but their reliability depends on the assumption that hidden...

Dark ReadingSecurity press
So Many AI Security Benchmarks, but None Tell the Whole Story
Measuring AI model security gets complex, fast, thanks to a growing patchwork of benchmarks targeting different variables in the equation. But none replace testing against your own code and workflows.
Monday, 26 October4 days ago
Dark ReadingSecurity press
Risks & Rewards: How AI Is Redefining the CISO's Role
Nvidia security executive Mark Weatherford says CISOs must help business leaders weigh AI's pros and cons, and ensure those deploying it own the risks.
Dark ReadingSecurity press
In-the-Wild Attack Abuses AI Agents' Trust in Markdown
A new AI agent prompt injection technique exploits how coding assistants consume local instruction files, blurring the line between text documents and executable actions.
Dark ReadingSecurity press
'Gheist' Weaponizes GitHub Tokens to Steal Cloud Secrets
An ongoing supply chain attack is harvesting credentials and sensitive data from thousands of developer repositories.
Dark ReadingSecurity press
10 Software Security Practices Built for the Next 250 Years
This Cybersecurity Awareness Month's theme, "Securing the Next 250," asks us to look beyond vulnerabilities and consider what will make our digital systems resilient for generations.
Schneier on SecuritySecurity press
Bias in Qwen3-Coder Model
Interesting research : TL;DR: Chinese AI models now sit inside Western products, and some carry geopolitical triggers: tell the model who the code is for, and the security of what it writes changes. For the first time, we showed that...
Friday, 23 October7 days ago
Dark ReadingSecurity press
Trust Is Not What It Seems — and Fraudsters Are Counting on It
Threat actors don't need to rely on malware to breach organizations anymore. They're simply calling help desks and politely asking for access, with a little help from artificial intelligence.
Dark ReadingSecurity press
Exposed to PHP2Shell? Cyber Experts Weigh in With Advice
Fixing the critical PHP flaws is not as simple as clicking "Update." Here's how to assess your risk, and what you can do to protect yourself.
Dark ReadingSecurity press
AI Tools Are Generating Massive Attacks for Little Cost
One campaign targets 105 sites using open-weight models; in another, public models gained full domain control for $12. Cyber-defense will have to change.
Ars Technica securitySecurity press
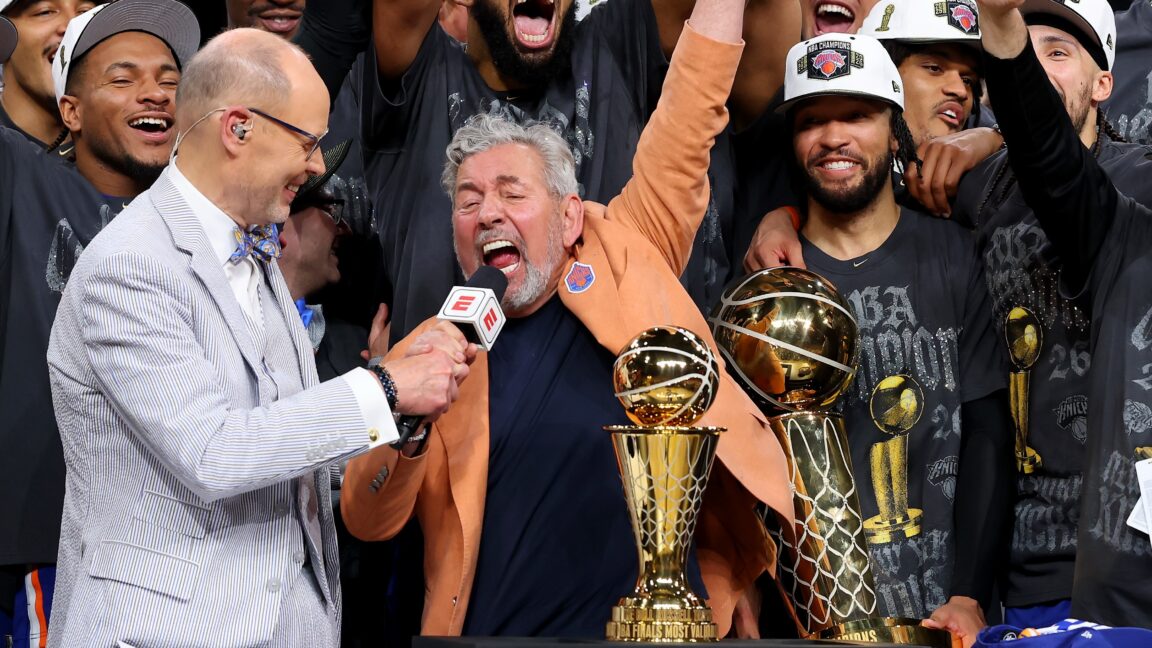
Knicks sent employees fake offer of championship rings in phishing test: Report
Corporate phishing tests are common, but this one was especially cruel.
Dark ReadingSecurity press
Why Caribbean Threats Cascade Into Global Cyber-Risk
The region is demonstrating what happens when exploits accelerate but assurance does not.
Schneier on SecuritySecurity press
Friday Squid Blogging: Increasing Squid Populations
This article in Nature argues that it’s due to an overfishing of predators and warming sea temperatures. As usual, you can also use this squid post to talk about the security stories in the news that I haven’t covered. Blog moderation...
Dark ReadingSecurity press
Cyber Insurance's New Reality: Underwriting Isn't Enough
Rising AI, social engineering, and cloud risks are pushing carriers beyond risk transfer and deeper into cybersecurity itself.
Dark ReadingSecurity press
AI Agents as Insider Threats: Inside Microsoft's Bet on a Unified Security Stack
Microsoft's Project Perception adds Guardian Agents to monitor and contain anomalous AI agents, but experts warn that policing unpredictable agents with other agents may compound — not contain — the risk.
Schneier on SecuritySecurity press
Compromised TLS Certificates
The Indian CA eMudhra Limited has eight TLS certificates with laughably weak private keys : The compromised eMudhra keys were defective at a level that’s challenging the imagination of many of the engineers studying the incident. A...
Dark ReadingSecurity press
State Bank of India Suffers a Customer PII Data Leak
Relatively small data breaches in India can turn quite serious, thanks to a sophisticated underground market for trading PII.
Thursday, 22 October8 days ago
Dark ReadingSecurity press
Microsoft Links Storm-0940 to ConnectWise Supply Chain Attack
The China-linked actor used an AI-enabled penetration-testing tool to automate and accelerate its attack on more than 2,200 tenants.
Dark ReadingSecurity press
What We Missed: Feds Lasso Texas Laptop Farms
In this video, Dark Reading editors discuss some of the news they didn't get a chance to cover, from busting up North Korea's stateside infrastructure in "Operation Lonestar Justice" to Staples' gift card bonanza.
Ars Technica securitySecurity press
Disgraced eMudhra drops out of TLS business after using cert private key of 4
Flubbed key signing "ceremony" allowed minting of web credentials for any site.
Dark ReadingSecurity press
Les supermarchés de l'UE paient d'un firmware de réfrigérateur non mis à jour
Des centaines de magasins ont subi des pertes se chiffrant en millions d'euros parce qu'ils avaient fait appel à des tiers pour gérer le micrologiciel OT obsolète qui pilotait leurs systèmes de climatisation.
Ars Technica securitySecurity press
Hackers got a four-day head start on epic PHP2Shell vulnerability
Hackers were already probing the bug before defenders were told it existed.
Dark ReadingSecurity press
As AI Risks Grow, Insurers Split on Covering the Damage
Some build specialized agentic AI coverage, while major carriers quietly exclude it — leaving enterprises exposed without their knowledge.
Schneier on SecuritySecurity press
New Serious PHP Vulnerabilities Released and Patched
PHP maintainers have released fixes for two critical vulnerabilities: PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35 fix two critical vulnerabilities that can allow unauthenticated remote code execution. All PHP users are strongly encouraged to...
Ars Technica securitySecurity press
333 Tor exit nodes hijacked to intercept SSH traffic and retrieve plaintext email
For 3 days this month, 333 exit nodes were hacked in hopes of stealing sensitive data.
Dark ReadingSecurity press
UAE Transitions 50% of Government Services to Agentic AI
The United Arab Emirates says it's creating a foundation of security and safety as it transforms its public service footprint.